

Real Exam Questions NSE4_FGT-6.4 Dumps Exam Questions in here [Sep-2021]
Get Latest Sep-2021 Conduct effective penetration tests using NSE4_FGT-6.4
NEW QUESTION 73
A network administrator is configuring a new IPsec VPN tunnel on FortiGate. The remote peer IP address is dynamic. In addition, the remote peer does not support a dynamic DNS update service.
What type of remote gateway should the administrator configure on FortiGate for the new IPsec VPN tunnel to work?
- A. Static IP Address
- B. Dialup User
- C. Dynamic DNS
- D. Pre-shared Key
Answer: B
NEW QUESTION 74
Which engine handles application control traffic on the next-generation firewall (NGFW) FortiGate?
- A. Detection engine
- B. Intrusion prevention system engine
- C. Antivirus engine
- D. Flow engine
Answer: B
NEW QUESTION 75
Which statement correctly describes NetAPI polling mode for the FSSO collector agent?
- A. The NetSessionEnum functionis user] to track user logouts.
- B. The collector agent must search security event logs.
- C. The collector agent uses a Windows API to query DCs for user logins.
- D. NetAPI polling can increase bandwidth usage in large networks.
Answer: C
NEW QUESTION 76
Refer to the exhibit.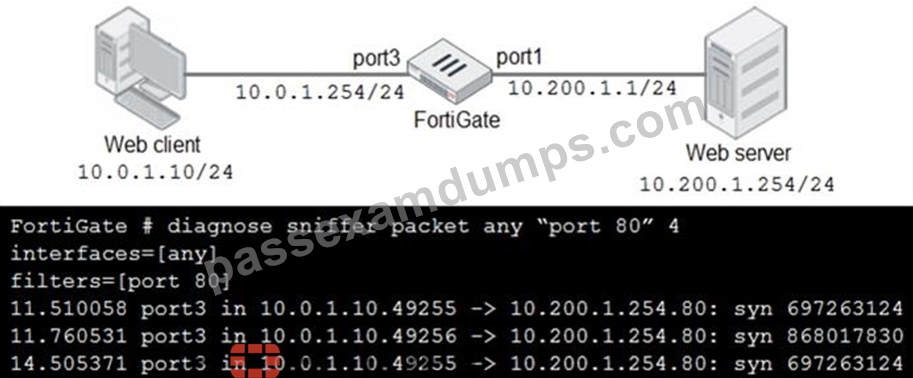
In the network shown in the exhibit, the web client cannot connect to the HTTP web server. The administrator runs the FortiGate built-in sniffer and gets the output as shown in the exhibit.
What should the administrator do next to troubleshoot the problem?
- A. Capture the traffic using an external sniffer connected to port1.
- B. Execute another sniffer in the FortiGate, this time with the filter "host 10.0.1.10"
- C. Run a sniffer on the web server.
- D. Execute a debug flow.
Answer: D
NEW QUESTION 77
Which two protocols are used to enable administrator access of a FortiGate device? (Choose two.)
- A. HTTPS
- B. FortiTelemetry
- C. SSH
- D. FTM
Answer: A,C
Explanation:
Explanation/Reference: https://docs.fortinet.com/document/fortigate/6.4.0/hardening-your-fortigate/995103/building- security-into-fortios
NEW QUESTION 78
A network administrator wants to set up redundant IPsec VPN tunnels on FortiGate by using two IPsec VPN tunnels and static routes.
* All traffic must be routed through the primary tunnel when both tunnels are up.
* The secondary tunnel must be used only if the primary tunnel goes down.
* In addition, FortiGate should be able to detect a dead tunnel to speed up tunnel failover.
Which two key configuration changes are needed on FortiGate to meet the design requirements? (Choose two.)
- A. Enable Auto-negotiate and Autokey Keep Alive on the phase 2 configuration of both tunnels.
- B. Configure a high distance on the static route for the primary tunnel, and a lower distance on the static route for the secondary tunnel.
- C. Enable Dead Peer Detection.
- D. Configure a lower distance on the static route for the primary tunnel, and a higher distance on the static route for the secondary tunnel.
Answer: A,C
NEW QUESTION 79
Which two policies must be configured to allow traffic on a policy-based next-generation firewall (NGFW) FortiGate? (Choose two.)
- A. SSL inspection and authentication policy
- B. Firewall policy
- C. Policy rule
- D. Security policy
Answer: B,C
NEW QUESTION 80
Which of the following statements correctly describes FortiGates route lookup behavior when searching for a suitable gateway? (Choose two)
- A. Lookup is done on every packet, regardless of direction
- B. Lookup is done on the first packet from the session originator
- C. Lookup is done on the trust reply packet from the responder
- D. Lookup is done on the last packet sent from the responder
Answer: B,C
NEW QUESTION 81
Examine the network diagram shown in the exhibit, and then answer the following question: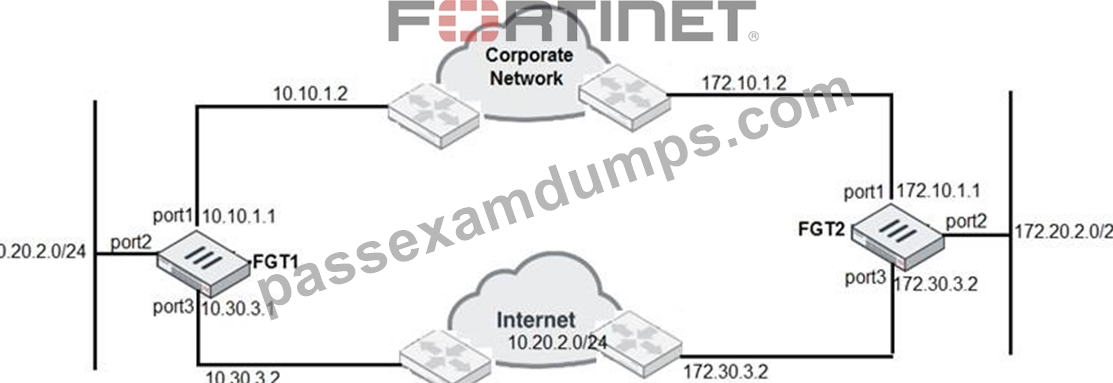
A firewall administrator must configure equal cost multipath (ECMP) routing on FGT1 to ensure both port1 and port3 links are used at the same time for all traffic destined for 172.20.2.0/24. Which of the following static routes will satisfy this requirement on FGT1? (Choose two.)
- A. 172.20.2.0/24 (1/150) via 10.30.3.2, port3 [10/0]
- B. 172.20.2.0/24 (1/0) via 10.10.1.2, port1 [0/0]
- C. 172.20.2.0/24 (1/150) via 10.10.3.2, port3 [10/0]
- D. 172.20.2.0/24 (25/0) via 10.10.3.2, port3 [5/0]
Answer: A,C
NEW QUESTION 82
Examine the IPS sensor configuration shown in the exhibit, and then answer the question below.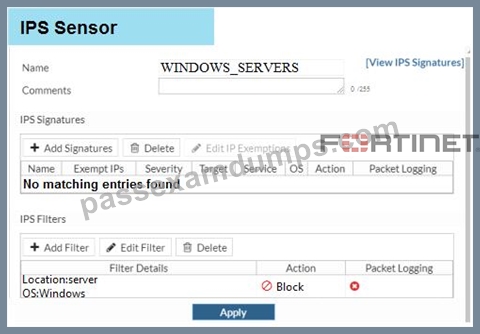
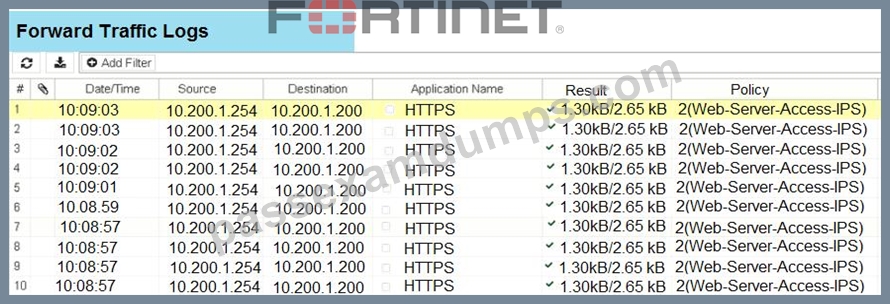
An administrator has configured the WINDOWS_SERVERS IPS sensor in an attempt to determine whether the influx of HTTPS traffic is an attack attempt or not. After applying the IPS sensor, FortiGate is still not generating any IPS logs for the HTTPS traffic.
What is a possible reason for this?
- A. The firewall policy is not using a full SSL inspection profile.
- B. A DoS policy should be used, instead of an IPS sensor.
- C. The IPS filter is missing the Protocol: HTTPS option.
- D. The HTTPS signatures have not been added to the sensor.
- E. A DoS policy should be used, instead of an IPS sensor.
Answer: A
NEW QUESTION 83
Which of the following statements about backing up logs from the CLI and downloading logs from the GUI are true? (Choose two.)
- A. Log downloads from the GUI are limited to the current filter view
- B. Log downloads from the GUI are stored as LZ4 compressed files.
- C. Log backups from the CLI cannot be restored to another FortiGate.
- D. Log backups from the CLI can be configured to upload to FTP as a scheduled time
Answer: A,C
NEW QUESTION 84
Refer to the exhibit.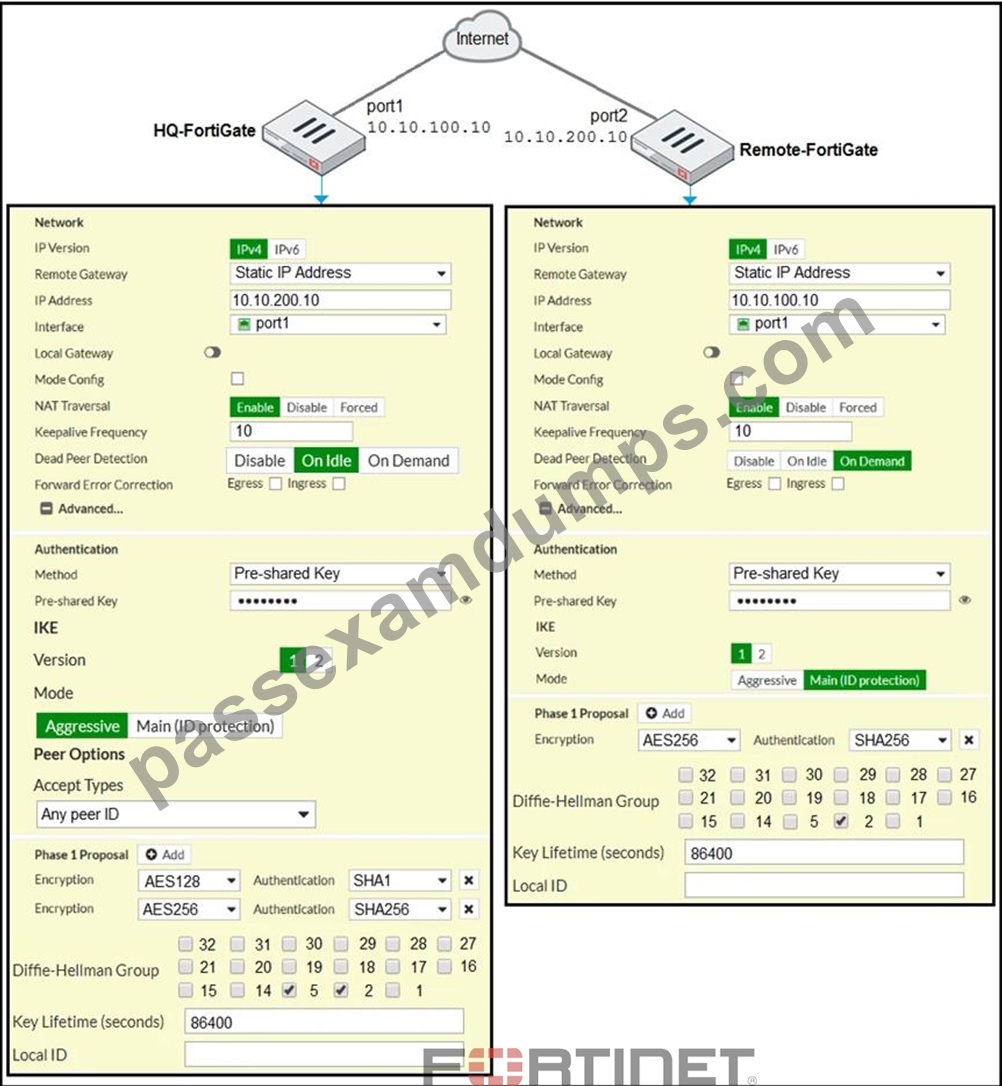
A network administrator is troubleshooting an IPsec tunnel between two FortiGate devices. The administrator has determined that phase 1 fails to come up. The administrator has also re-entered the pre-shared key on both FortiGate devices to make sure they match.
Based on the phase 1 configuration and the diagram shown in the exhibit, which two configuration changes will bring phase 1 up? (Choose two.)
- A. On HQ-FortiGate, set IKE mode to
- B. On Remote-FortiGate, set port2
- C. On HQ-FortiGate, disable Diffie-Helman group 2
- D. On both FortiGate devices, set
Answer: A,D
NEW QUESTION 85
Examine the IPS sensor and DoS policy configuration shown in the exhibit, then answer the question below.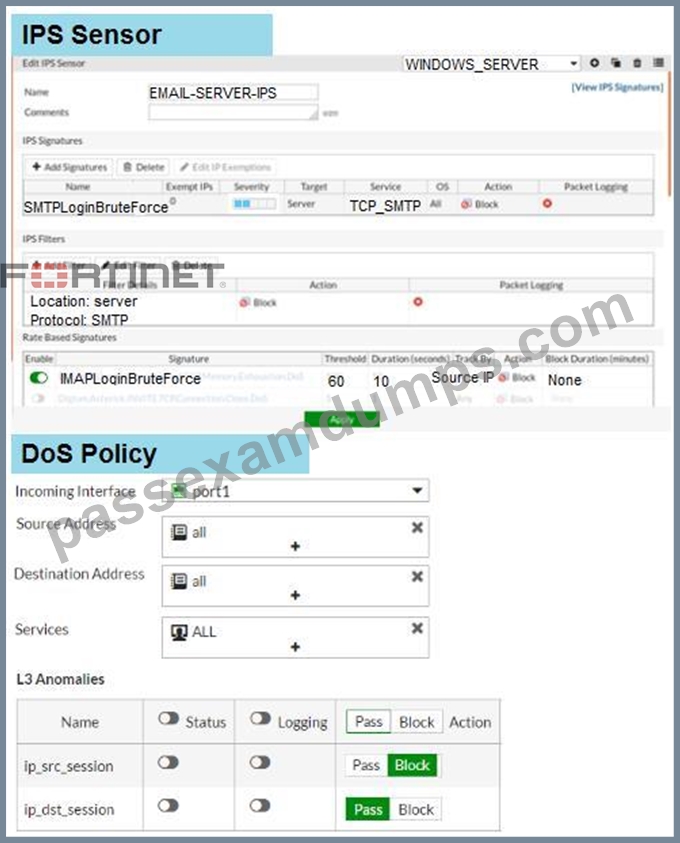
When detecting attacks, which anomaly, signature, or filter will FortiGate evaluate first?
- A. ip_src_session
- B. IMAP.Login.brute.Force
- C. Location: server Protocol: SMTP
- D. SMTP.Login.Brute.Force
Answer: B
NEW QUESTION 86
An administrator is running the following sniffer command:
Which three pieces of Information will be Included in me sniffer output? {Choose three.)
- A. Interface name
- B. Ethernet header
- C. Application header
- D. IP header
- E. Packet payload
Answer: B,C,E
NEW QUESTION 87
Refer to the exhibit.
Exhibit A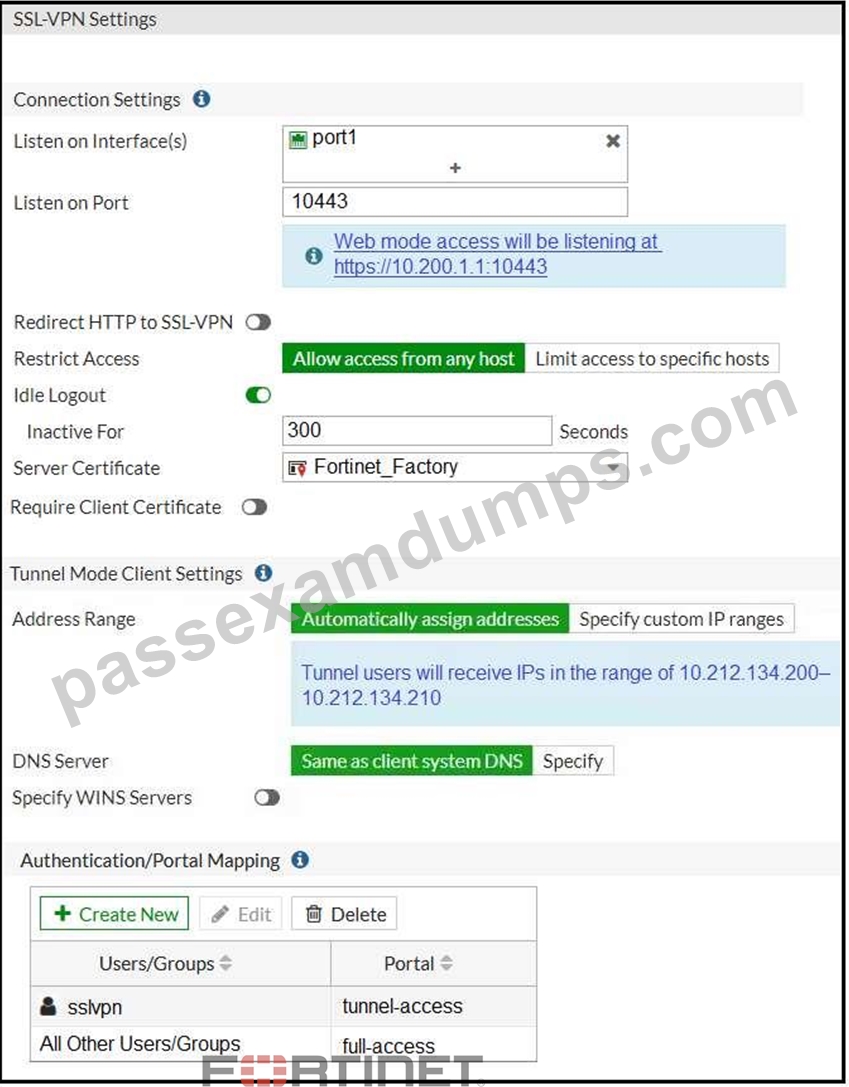
Exhibit B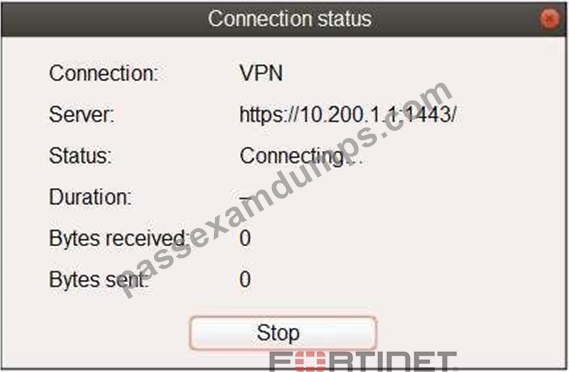
The SSL VPN connection fails when a user attempts to connect to it.
What should the user do to successfully connect to SSL VPN?
- A. Change the idle-timeout.
- B. Change the Server IP address.
- C. Change the SSL VPN port on the client.
- D. Change the SSL VPN portal to the tunnel.
Answer: C
Explanation:
Explanation/Reference: https://docs.fortinet.com/document/fortigate/5.4.0/cookbook/150494
NEW QUESTION 88
Refer to the exhibit.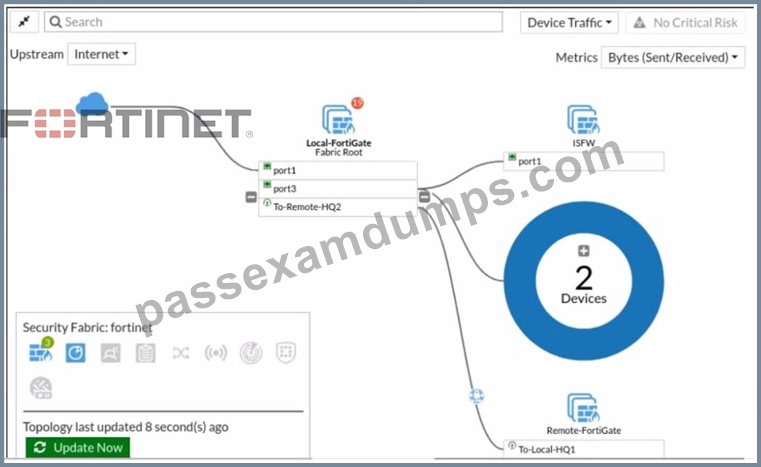
Given the security fabric topology shown in the exhibit, which two statements are true? (Choose two.)
- A. Device detection is disabled on all FortiGate devices.
- B. There are 19 security recommendations for the security fabric.
- C. There are five devices that are part of the security fabric.
- D. This security fabric topology is a logical topology view.
Answer: A,B
NEW QUESTION 89
A network administrator has enabled SSL certificate inspection and antivirus on FortiGate. When downloading an EICAR test file through HTTP, FortiGate detects the virus and blocks the file. When downloading the same file through HTTPS, FortiGate does not detect the virus and the file can be downloaded.
What is the reason for the failed virus detection by FortiGate?
- A. SSL/SSH Inspection profile is incorrect
- B. Antivirus definitions are not up to date
- C. Application control is not enabled
- D. Antivirus profile configuration is incorrect
Answer: A
NEW QUESTION 90
......
Authentic Best resources for NSE4_FGT-6.4 Online Practice Exam: https://www.passexamdumps.com/NSE4_FGT-6.4-valid-exam-dumps.html
