

Free 2021 CCNP Security 300-720 dumps are available on Google Drive shared by PassExamDumps
Welcome to download the newest PassExamDumps 300-720 PDF dumps: https://www.passexamdumps.com/300-720-valid-exam-dumps.html ( 92 Q&As)
NEW QUESTION 27
An engineer is tasked with reviewing mail logs to confirm that messages sent from domain abc.com are passing SPF verification and being accepted by the Cisco ESA. The engineer notices that SPF verification is not being performed and that SPF is not being referenced in the logs for messages sent from domain abc.com.
Why is the verification not working properly?
- A. The SPF conformance level is set to SIDF compatible on the Mail Flow Policy.
- B. SPF verification is disabled on the Mail Flow Policy.
- C. An SPF verification Content Filter has not been created.
- D. SPF verification is disabled in the Recipient Access Table.
Answer: C
NEW QUESTION 28
What is a benefit of implementing URL filtering on the Cisco ESA?
- A. blacklists spam
- B. removes threats from malicious URLs
- C. enhances reputation against malicious URLs
- D. provides URL reputation protection
Answer: D
Explanation:
Reference:
https://www.cisco.com/c/en/us/support/docs/security/email-security-appliance/118775-technote- esa-00.html
NEW QUESTION 29
Which two features are applied to either incoming or outgoing mail policies? (Choose two.)
- A. sender reputation filtering
- B. antivirus
- C. outbreak filters
- D. application filtering
- E. Indication of Compromise
Answer: B,C
NEW QUESTION 30
Which method enables an engineer to deliver a flagged message to a specific virtual gateway address in the most flexible way?
- A. Map the envelope sender address to the host.
- B. Issue the altsrchost command.
- C. Set up the interface group with the flag.
- D. Apply a filter on the message.
Answer: B
Explanation:
Explanation/Reference: https://www.cisco.com/c/en/us/td/docs/security/esa/esa11-1/user_guide/ b_ESA_Admin_Guide_11_1/b_ESA_Admin_Guide_chapter_01000.html#con_1133810
NEW QUESTION 31
A Cisco ESA administrator has several mail policies configured. While testing policy match using a specific sender, the email was not matching the expected policy.
What is the reason of this?
- A. The Tram* header is checked against all policies in a top-down fashion.
- B. The message header with the highest priority is checked against each policy in a top-down fashion.
- C. The To" header is checked against all policies in a top-down fashion.
- D. The message header with the highest priority is checked against the Default policy in a top-down fashion.
Answer: D
NEW QUESTION 32
How does the graymail safe unsubscribe feature function?
- A. It checks the reputation of the URI and performs the unsubscribe process on behalf of the end user.
- B. It redirects the end user who clicks the unsubscribe button to a sandbox environment to allow a safe unsubscribe.
- C. It checks the URI reputation and category and allows the content filter to take an action on it.
- D. It strips the malicious content of the URI before unsubscribing.
Answer: A
Explanation:
Explanation/Reference: https://www.cisco.com/c/en/us/support/docs/security/email-security-appliance/200383- Graymail-Detection-and-Safe-Unsubscribin.html
NEW QUESTION 33
Which two statements about configuring message filters within the Cisco ESA are true? (Choose two.)
- A. The filterconfig command executed from the CLI is used to configure message filters.
- B. Message filters can be configured only from the CLI.
- C. Message filters configuration within the web user interface is located within Incoming Content Filters.
- D. The filters command executed from the CLI is used to configure the message filters.
- E. Message filters can be configured only from the web user interface.
Answer: B,D
Explanation:
Explanation/Reference:
Reference: https://www.cisco.com/c/en/us/support/docs/security/email-security-appliance/213940-esa- using-a-message-filter-to-take-act.html
NEW QUESTION 34
Which two steps configure Forged Email Detection? (Choose two.)
- A. Configure a filter to check the Header From value against the Forged Email Detection dictionary.
- B. Configure a content dictionary with executive email addresses.
- C. Configure a content dictionary with friendly names.
- D. Configure a filter to use the Forged Email Detection rule and dictionary.
- E. Enable Forged Email Detection on the Security Services page.
Answer: B,D
Explanation:
Explanation/Reference: https://explore.cisco.com/esa-feature-enablement/user-guide-for-async-11
NEW QUESTION 35 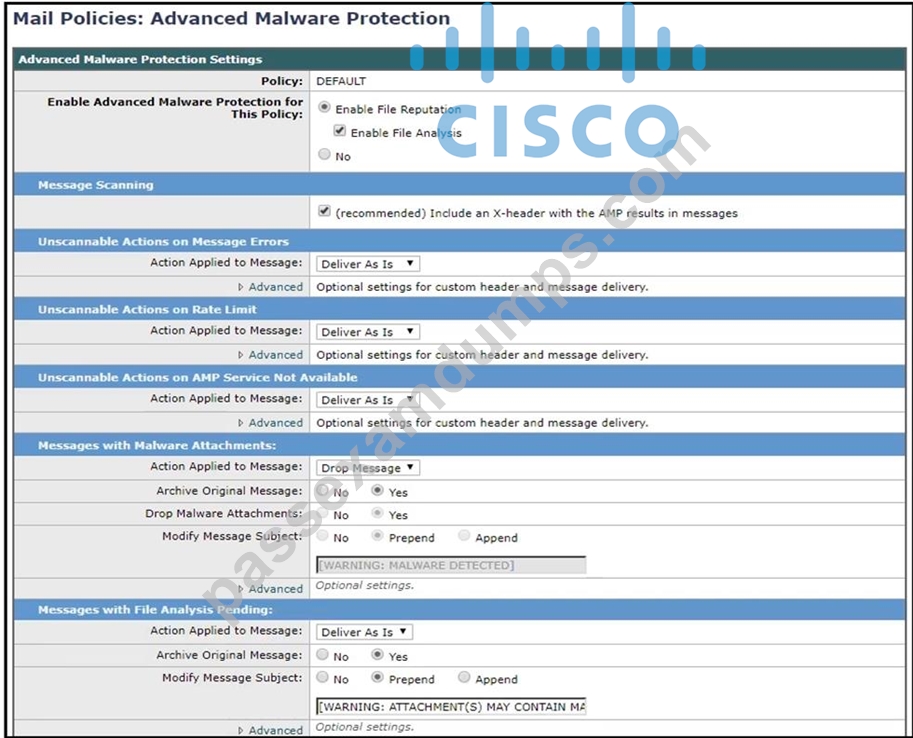
Refer to the exhibit. How should this configuration be modified to stop delivering Zero Day malware attacks?
- A. Change Unscannable Action from Deliver As Is to Quarantine.
- B. Apply Prepend on Modify Message Subject under Malware Attachments.
- C. Change File Analysis Pending action from Deliver As Is to Quarantine.
- D. Configure mailbox auto-remediation.
Answer: D
NEW QUESTION 36
Which action must be taken before a custom quarantine that is being used can be deleted?
- A. Delete only the unused quarantine.
- B. Remove the quarantine from the message action of a filter.
- C. Delete the quarantine that is not assigned to a filter.
- D. Delete the quarantine that is assigned to a filter.
Answer: B
NEW QUESTION 37
A Cisco ESA administrator has noticed that new messages being sent to the Centralized Policy Quarantine are being released after one hour. Previously, they were being held for a day before being released.
What was configured that caused this to occur?
- A. The threshold settings were set to default.
- B. The threshold settings were set to override the clock settings.
- C. The retention period was changed to one hour.
- D. The retention period was set to default.
Answer: A
NEW QUESTION 38 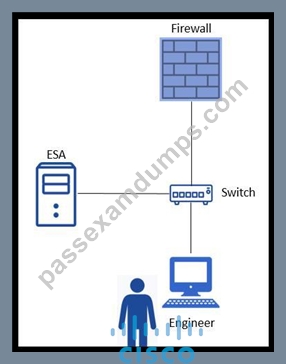
Refer to the exhibit. An engineer is trying to connect to a Cisco ESA using SSH and has been unsuccessful.
Upon further inspection, the engineer notices that there is a loss of connectivity to the neighboring switch.
Which connection method should be used to determine the configuration issue?
- A. Ethernet
- B. HTTPS
- C. serial
- D. Telnet
Answer: C
NEW QUESTION 39
Which SMTP extension does Cisco ESA support for email security?
- A. ETRN
- B. STARTTLS
- C. UTF8SMTP
- D. PIPELINING
Answer: B
NEW QUESTION 40
How does the graymail safe unsubscribe feature function?
- A. It checks the reputation of the URI and performs the unsubscribe process on behalf of the end user.
- B. It redirects the end user who clicks the unsubscribe button to a sandbox environment to allow a safe unsubscribe.
- C. It checks the URI reputation and category and allows the content filter to take an action on it.
- D. It strips the malicious content of the URI before unsubscribing.
Answer: A
NEW QUESTION 41
Which type of query must be configured when setting up the Spam Quarantine while merging notifications?
- A. Spam Quarantine Alias Consolidation Query
- B. Spam Quarantine Alias Masquerading Query
- C. Spam Quarantine Alias Authentication Query
- D. Spam Quarantine Alias Routing Query
Answer: A
NEW QUESTION 42
Which two statements about configuring message filters within the Cisco ESA are true? (Choose two.)
- A. The filterconfig command executed from the CLI is used to configure message filters.
- B. Message filters can be configured only from the CLI.
- C. Message filters configuration within the web user interface is located within Incoming Content Filters.
- D. The filters command executed from the CLI is used to configure the message filters.
- E. Message filters can be configured only from the web user interface.
Answer: B,D
Explanation:
Reference:
https://www.cisco.com/c/en/us/support/docs/security/email-security-appliance/213940-esa-using-a- message-filter-to-take-act.html
NEW QUESTION 43
Which type of attack is prevented by configuring file reputation filtering and file analysis features?
- A. backscatter
- B. zero-day
- C. phishing
- D. denial of service
Answer: B
Explanation:
Reference:
https://www.cisco.com/c/en/us/td/docs/security/esa/esa12-0/user_guide/ b_ESA_Admin_Guide_12_0/b_ESA_Admin_Guide_chapter_010000.html#con_1809885
NEW QUESTION 44
Drag and drop the steps to configure Cisco ESA to use SPF/SIDF verification from the left into the correct order on the right.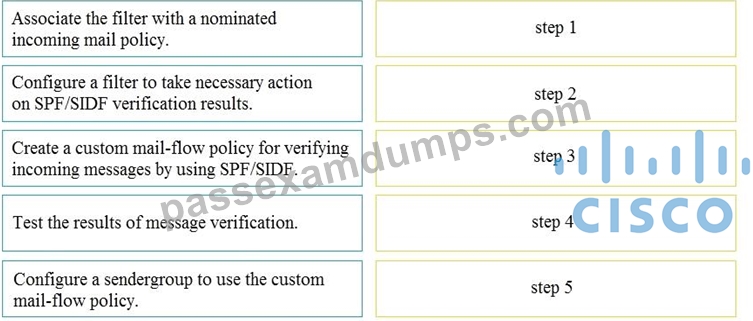
Answer:
Explanation: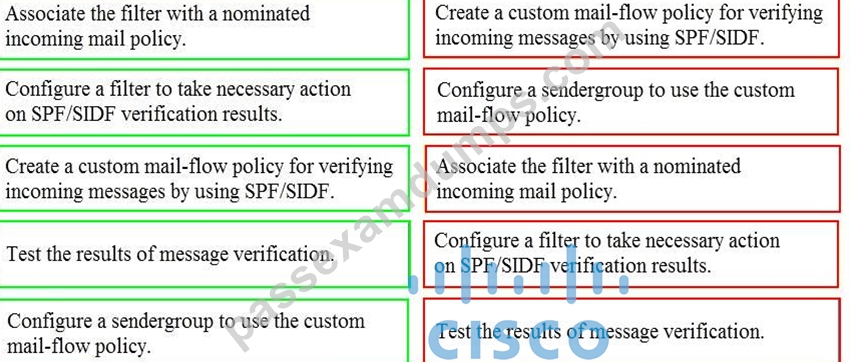
NEW QUESTION 45
Which feature must be configured before an administrator can use the outbreak filter for nonviral threats?
- A. data loss prevention
- B. antivirus
- C. quarantine threat level
- D. antispam
Answer: D
Explanation:
Reference:
https://www.cisco.com/c/en/us/td/docs/security/esa/esa12-0/user_guide/ b_ESA_Admin_Guide_12_0/b_ESA_Admin_Guide_chapter_01110.html
NEW QUESTION 46
An engineer is testing mail flow on a new Cisco ESA and notices that messages for domain abc.com are stuck in the delivery queue. Upon further investigation, the engineer notices that the messages pending delivery are destined for 192.168.1.11, when they should instead be routed to 192.168.1.10.
What configuration change needed to address this issue?
- A. Modify the SMTP route for the domain and change the IP address to 192.168.1.10.
- B. Modify Destination Controls entry for the domain abc.com.
- C. Add an address list for domain abc.com.
- D. Modify the Routing Tables and add a route for IP address to 192.168.1.10.
Answer: A
NEW QUESTION 47
An organization wants to use its existing Cisco ESA to host a new domain and enforce a separate corporate policy for that domain.
What should be done on the Cisco ESA to achieve this?
- A. Use the altrchost command to add a separate gateway for the new domain.
- B. Use the dsestconf command to add a separate destination for the new domain.
- C. Use the smtproutes command to configure a SMTP route for the new domain.
- D. Use the deli very config command to configure mail delivery for the new domain.
Answer: C
NEW QUESTION 48
Which action is a valid fallback when a client certificate is unavailable during SMTP authentication on Cisco ESA?
- A. LDAP BIND
- B. SMTP AUTH
- C. SMTP TLS
- D. LDAP Query
Answer: B
Explanation:
Explanation/Reference: https://www.cisco.com/c/en/us/td/docs/security/esa/esa12-0/user_guide/ b_ESA_Admin_Guide_12_0/b_ESA_Admin_Guide_12_0_chapter_011011.html
NEW QUESTION 49
When email authentication is configured on Cisco ESA, which two key types should be selected on the signing profile? (Choose two.)
- A. DKIM
- B. Private Keys
- C. Symmetric Keys
- D. Public Keys
- E. Domain Keys
Answer: A,E
NEW QUESTION 50
Spreadsheets containing credit card numbers are being allowed to bypass the Cisco ESA.
Which outgoing mail policy feature should be configured to catch this content before it leaves the network?
- A. data loss prevention
- B. file analysis
- C. file reputation filtering
- D. outbreak filtering
Answer: D
NEW QUESTION 51
When DKIM signing is configured, which DNS record must be updated to load the DKIM public signing key?
- A. AAAA record
- B. MX record
- C. TXT record
- D. PTR record
Answer: C
Explanation:
Explanation/Reference: https://www.cisco.com/c/en/us/support/docs/security/email-security-appliance/213939-esa- configure-dkim-signing.html
NEW QUESTION 52
......
Tested Material Used To 300-720: https://www.passexamdumps.com/300-720-valid-exam-dumps.html
Following are some new 300-720 Real Exam Questions!: https://drive.google.com/open?id=1iJyKo9X5UmXAwbAuimPysrpj7dk3pQoo
