

2024 Provide Updated Microsoft MS-500 Dumps as Practice Test and PDF
MS-500 Dumps are Available for Instant Access
Prerequisites
The candidates for this certification test should be familiar with a range of Microsoft 365 workloads. They also need to have excellent experience and skills in identity protection, security management, data governance, information protection, and threat protection. They should understand Microsoft 365 and hybrid environments before attempting the exam.
NEW QUESTION # 191
Please wait while the virtual machine loads. Once loaded, you may proceed to the lab section. This may take a few minutes, and the wait time will not be deducted from your overall test time.
When the Next button is available, click it to access the lab section. In this section, you will perform a set of tasks in a live environment. While most functionality will be available to you as it would be in a live environment, some functionality (e.g., copy and paste, ability to navigate to external websites) will not be possible by design.
Scoring is based on the outcome of performing the tasks stated in the lab. In other words, it doesn't matter how you accomplish the task, if you successfully perform it, you will earn credit for that task.
Labs are not timed separately, and this exam may more than one lab that you must complete. You can use as much time as you would like to complete each lab. But, you should manage your time appropriately to ensure that you are able to complete the lab(s) and all other sections of the exam in the time provided.
Please note that once you submit your work by clicking the Next button within a lab, you will NOT be able to return to the lab.
Username and password
Use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password, place your cursor in the Enter password box and click on the password below.
Microsoft 365 Username:
admin@[email protected]
Microsoft 365 Password: &=Q8v@2qGzYz
If the Microsoft 365 portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support only:
Lab instance: 11032396
You need to ensure that when users tag documents as classified, a classified watermark is applied to the documents.
To complete this task, sign in to the Microsoft Office 365 admin center.
Answer:
Explanation:
See explanation below.
Explanation
1. In the admin center, select the Compliance
2. Select Classification > Sensitivity labels
3. Select Create a label, and when the warning appears, select
4. Enter a Label name, Tooltip, and
5. Turn on Encryption. Choose when you want to assign permissions, whether you want your users' access to the content to expire, and whether you want to allow offline access.
6. Select Assign permissions > Add these email addresses or domains.
7. Enter an email address or domain name (such as Contoso.org). Select Add, and repeat for each email address or domain you want to add.
8. Select Choose permissions from preset or custom.
9. Use the drop-down list to select preset permissions, such as Reviewer or Viewer, or select Custom permissions. If you chose Custom, select the permissions from the list. Select Save >Save > Next.
10. Turn on Content marking, and choose the markings you want to use.
11. For each marking that you choose, select Customize text. Enter the text you want to appear on the document, and set the font and layout options. Select Save, and then repeat for any additional markings. Select Next.
12. Optionally, turn on Endpoint data loss prevention. Select Next.
13. Optionally, turn on Auto labeling. Add a condition. For example, under Detect content that contains, select Add a condition. Enter the condition; for example, add a condition that if passport, Social Security, or other sensitive information is detected, the label will be added. Select Next.
14. Review your settings, and select Create. Your label has been created. Repeat this process for any additional labels you want.
15. By default, labels appear in Office apps in this order: , and Public. To change the order, for each label, select More actions (the ellipsis), and then move the label up or down. Typically, permissions are listed from the lowest to highest level of permissions.
16. To add a sub-label to a label, select
17. When finished, choose Publish labels . Select the labels you want to publish, and then select Add > Done
18. By default, the new label policy is applied to everyone. If you want to limit who the policy is applied to, select Choose users or groups > . Select who you want the policy to apply to, and then select Add > Done > Next.
19. If you want a default label for documents and email, select the label you want from the drop-down list.
Review the remaining settings, adjust as needed, and then select
20. Enter a Name and Description
21. Review your settings, then select
Reference:
https://support.office.com/en-us/article/create-and-manage-sensitivity-labels-2fb96b54-7dd2-4f0c-ac8d-170790d
https://docs.microsoft.com/en-us/microsoft-365/compliance/sensitivity-labels?view=o365-worldwide
NEW QUESTION # 192
Please wait while the virtual machine loads. Once loaded, you may proceed to the lab section. This may take a few minutes, and the wait time will not be deducted from your overall test time.
When the Next button is available, click it to access the lab section. In this section, you will perform a set of tasks in a live environment. While most functionality will be available to you as it would be in a live environment, some functionality (e.g., copy and paste, ability to navigate to external websites) will not be possible by design.
Scoring is based on the outcome of performing the tasks stated in the lab. Inother words, it doesn't matter how you accomplish the task, if you successfully perform it, you will earn credit for that task.
Labs are not timed separately, and this exam may more than one lab that you must complete. You can use as much time as you would like to complete each lab. But, you should manage your time appropriately to ensure that you are able to complete the lab(s) and all other sections of the exam in the time provided.
Please note that once you submit your work by clicking the Next buttonwithin a lab, you will NOT be able to return to the lab.
Username and password
Use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter yourpassword, place your cursor in the Enter password box and click on the password below.
Microsoft 365 Username:
admin@[email protected]
Microsoft 365 Password:&=Q8v@2qGzYz
If the Microsoft 365 portal does not load successfully in the browser,press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support only:
Lab instance:11032396
You need to ensure that a global administrator is notified when a document that contains U.S. Health Insurance Portability and Accountability Act (HIPAA) data is identified in your Microsoft 365 tenant.
To complete this task, sign in to the Microsoft Office 365 admin center.
Answer:
Explanation:
See explanation below.
Explanation
1. In the Security & Compliance Center > left navigation >Data loss prevention>Policy>+ Create a policy.
2. Choose the U.S. Health Insurance Portability and Accountability Act (HIPAA) template >Next.
3. Name the policy >Next.
4. ChooseAll locations in Office 365
5. At the firstPolicy Settingsstep just accept the defaults,
6. After clickingNext,you'll be presented with an additional
Deselect the Show policy tips to users and send them an email notification option.
Select the Detectwhen content that's being shared contains option, and decrease the number of instances to 1.
Select the Send incident reports in email option.
7. >Next
8. Select the option to turn on the policy right away >Next.
9. ClickCreateto finish creating the policy.
References:
https://docs.microsoft.com/en-us/microsoft-365/compliance/create-test-tune-dlp-policy?view=o365-worldwide
https://docs.microsoft.com/en-us/microsoft-365/compliance/data-loss-prevention-policies?view=o365-worldwid
https://docs.microsoft.com/en-us/microsoft-365/compliance/what-the-dlp-policy-templates-include?view=o365
NEW QUESTION # 193
Your company has a Microsoft 365 subscription that contains the users shown in the following table.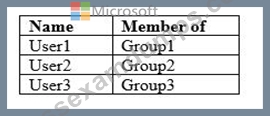
The company implements Windows Defender Advanced Threat Protection (Windows Defender ATP).
Windows Defender ATP includes the roles shown in the following table: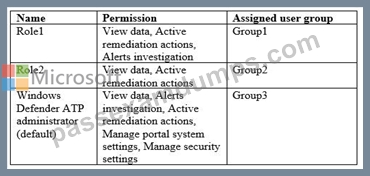
Windows Defender ATP contains the machine groups shown in the following table: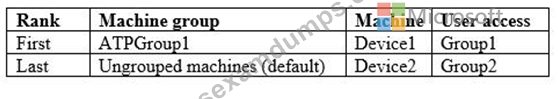
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.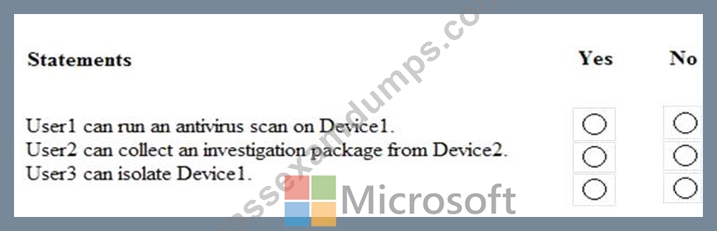
Answer:
Explanation: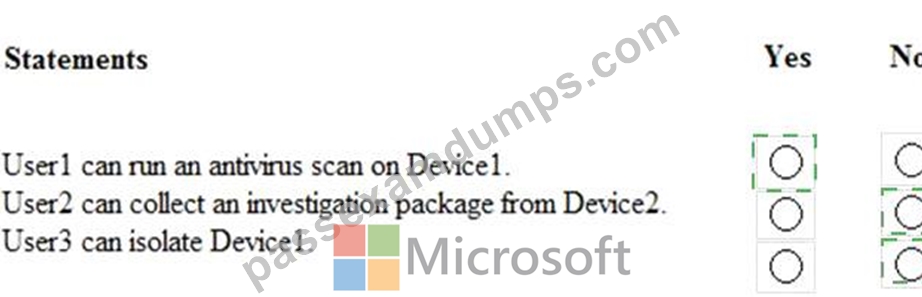
Explanation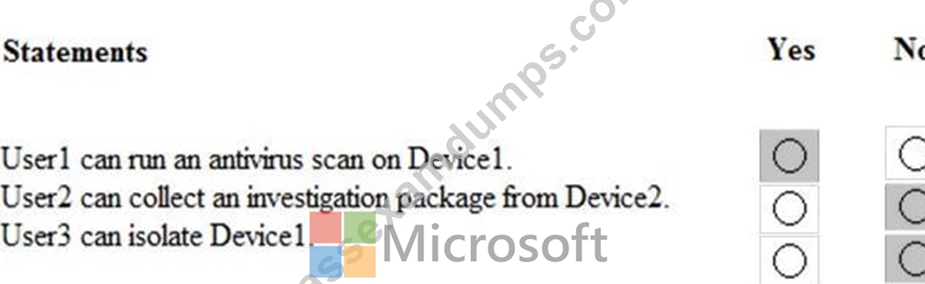
NEW QUESTION # 194
You have a Microsoft 365 E5 subscription.
You implement Advanced Threat Protection (ATP) safe attachments policies for all users.
User reports that email messages containing attachments take longer than expected to be received.
You need to reduce the amount of time it takes to receive email messages that contain attachments. The solution must ensure that all attachments are scanned for malware. Attachments that have malware must be blocked.
What should you do from ATP?
- A. Set the action to Block
- B. Add an exception
- C. Set the action to Dynamic Delivery
- D. Add a condition
Answer: C
Explanation:
Explanation/Reference:
https://docs.microsoft.com/en-us/office365/securitycompliance/dynamic-delivery-and-previewing
NEW QUESTION # 195
You have a Microsoft 365 E5 subscription.
From Microsoft Azure Active Directory (Azure AD), you create a security group named Group1. You add 10 users to Group1.
You need to apply app enforced restrictions to the members of Group1 when they connect to Microsoft Exchange Online from non-compliant devices, regardless of their location.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.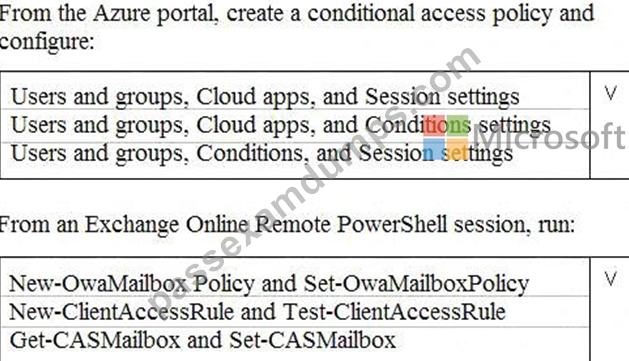
Answer:
Explanation: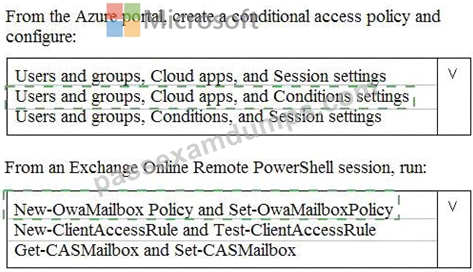
Explanation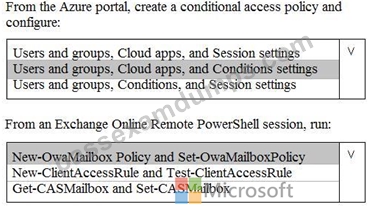
NEW QUESTION # 196
You have a Microsoft E5 subscription that contains two users named User 1 and User2.
You have a Microsoft SharePoint site named Site1. Site1 stores files that contain IP addresses as shown in the following table.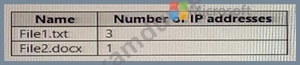
User1 is assigned the SharePoint admin role for Site1. User2 is a member of Sile1. You create the data loss prevention (DLP)1 policy shown in the following exhibit.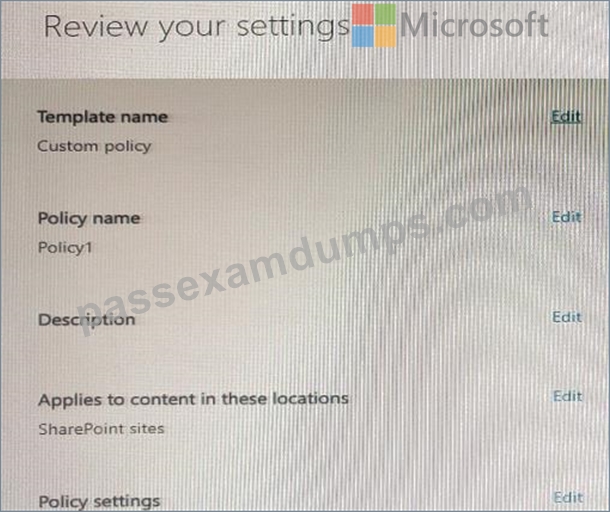
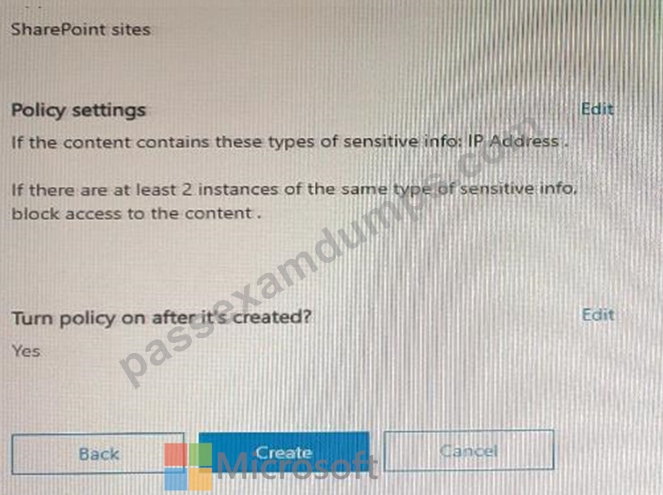
For each of the following statements, select Yes if the statement is true: Otherwise, select No. NOTE: Each correct selection is worth one point.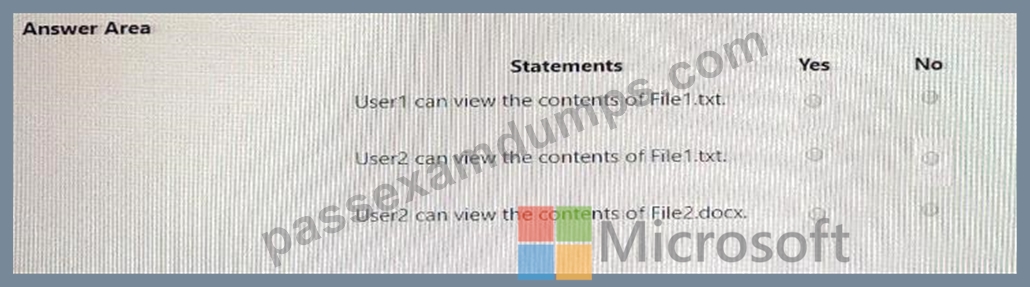
Answer:
Explanation: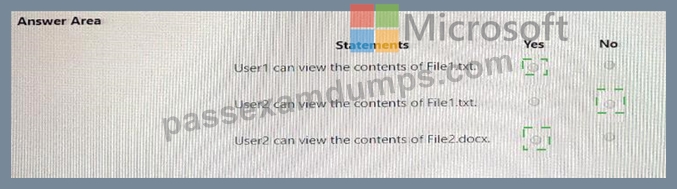
Explanation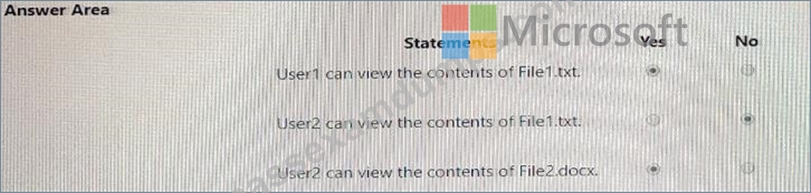
NEW QUESTION # 197
Your network contains an Active Directory domain named contoso.com. The domain contains a VPN server named VPN1 that runs Windows Server 2016 and has the Remote Access server role installed.
You have a Microsoft Azure subscription.
You are deploying Azure Advanced Threat Protection (ATP)
You install an Azure ATP standalone sensor on a server named Server1 that runs Windows Server 2016.
You need to integrate the VPN and Azure ATP.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.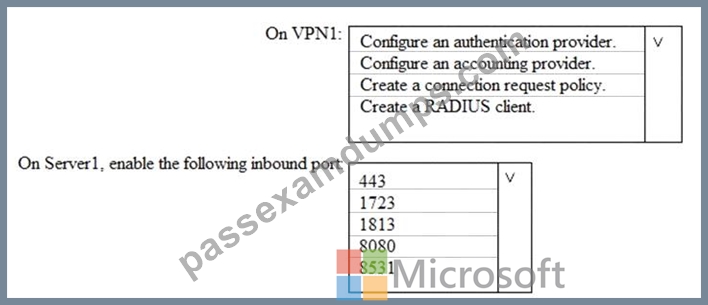
Answer:
Explanation: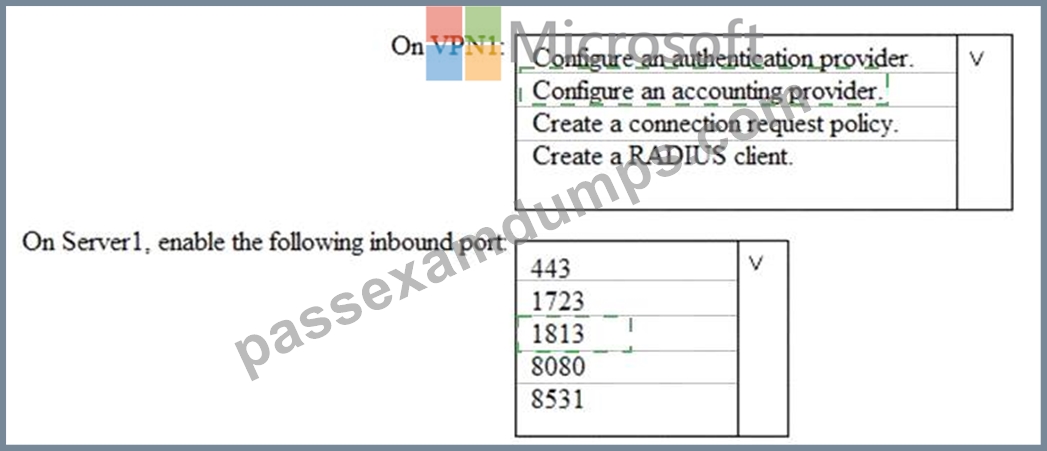
Explanation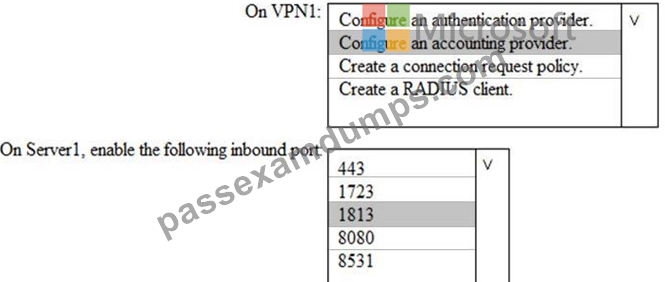
Reference:
https://docs.microsoft.com/en-us/azure-advanced-threat-protection/install-atp-step6-vpn
NEW QUESTION # 198
You need to ensure that a user named Grady Archie can monitor the service health of your Microsoft 365 tenant. The solution must use the principle of least privilege.
To complete this task, sign in to the Microsoft 365 portal.
Answer:
Explanation:
See explanation below.
Explanation
You need to assign the Service Administrator role to Grady Archie.
In the Microsoft 365 Admin Center,type Grady Archie into theSearch for users, groups, settings or taskssearch box.
Select the Grady Archie user account from the search results.
In theRolessection of the user account properties, click the
Select theCustomized Administrato option. This will display a list of admin roles.
Select theService adminrole.
ClickSaveto save the changes.
Reference:
https://docs.microsoft.com/en-us/office365/enterprise/view-service-health
NEW QUESTION # 199
You have a Microsoft 365 subscription.
A customer requests that you provide her with all documents that reference her by name.
You need to provide the customer with a copy of the content.
Which four actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.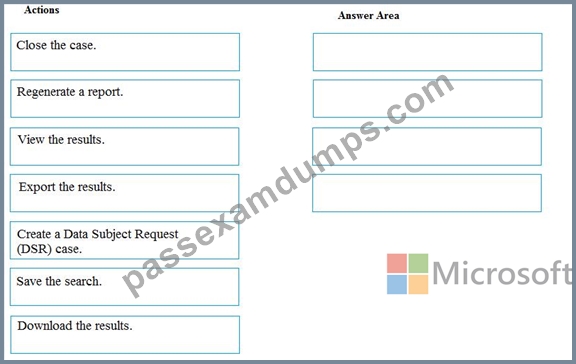
Answer:
Explanation: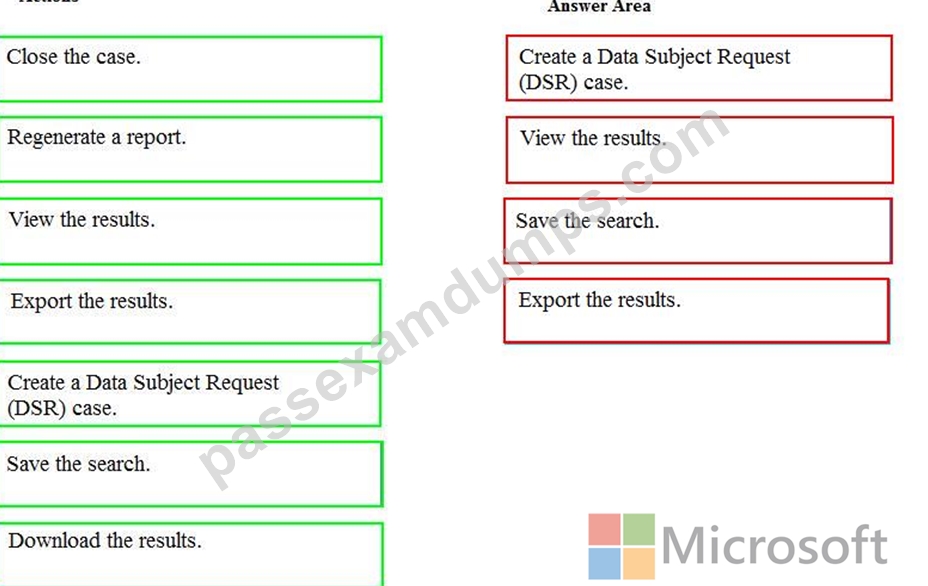
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/gdpr-dsr-office365
Topic 1, Fabrikam inc.
Overview
Fabrikam, Inc. is manufacturing company that sells products through partner retail stores. Fabrikam has 5,000 employees located in offices throughout Europe.
Existing Environment
Network Infrastructure
The network contains an Active Directory forest named fabrikam.com. Fabrikam has a hybrid Microsoft Azure Active Directory (Azure AD) environment.
The company maintains some on-premises servers for specific applications, but most end-user applications are provided by a Microsoft 365 E5 subscription.
Problem Statements
Fabrikam identifies the following issues:
* Since last Friday, the IT team has been receiving automated email messages that contain "Unhealthy Identity Synchronization Notification" in the subject line.
* Several users recently opened email attachments that contained malware. The process to remove the malware was time consuming.
Requirements
Planned Changes
4Fabrikam plans to implement the following changes:
* Fabrikam plans to monitor and investigate suspicious sign-ins to Active Directory
* Fabrikam plans to provide partners with access to some of the data stored in Microsoft 365 Application Administration Fabrikam identifies the following application requirements for managing workload applications:
* User administrators will work from different countries
* User administrators will use the Azure Active Directory admin center
* Two new administrators named Admin1 and Admin2 will be responsible for managing Microsoft Segment Exchange Online only Security Requirements Fabrikam identifies the following security requirements:
* Access to the Azure Active Directory admin center by the user administrators must be reviewed every seven days. If an administrator fails to respond to an access request within three days, access must be removed
* Users who manage Microsoft 365 workloads must only be allowed to perform administrative tasks for up to three hours at a time. Global administrators must be exempt from this requirement
* Users must be prevented from inviting external users to view company data. Only global administrators and a user named User1 must be able to send invitations
* Azure Advanced Threat Protection (ATP) must capture security group modifications for sensitive groups, such as Domain Admins in Active Directory
* Workload administrators must use multi-factor authentication (MFA) when signing in from an anonymous or an unfamiliar location
* The location of the user administrators must be audited when the administrators authenticate to Azure AD
* Email messages that include attachments containing malware must be delivered without the attachment
* The principle of least privilege must be used whenever possible
NEW QUESTION # 200
You have a Microsoft 365 subscription. From the Security & Compliance admin center, you create the retention policies shown in the following table.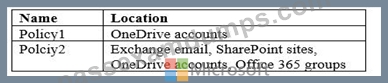
Policy1 if configured as showing in the following exhibit.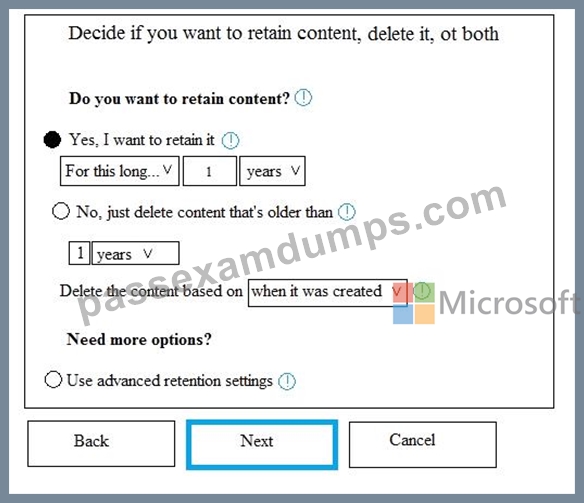
Policy2 is configured as shown in the following exhibit.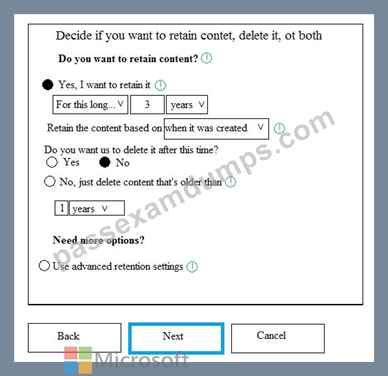
For each of the following statements, select Yes if the statement is true. Otherwise, select No.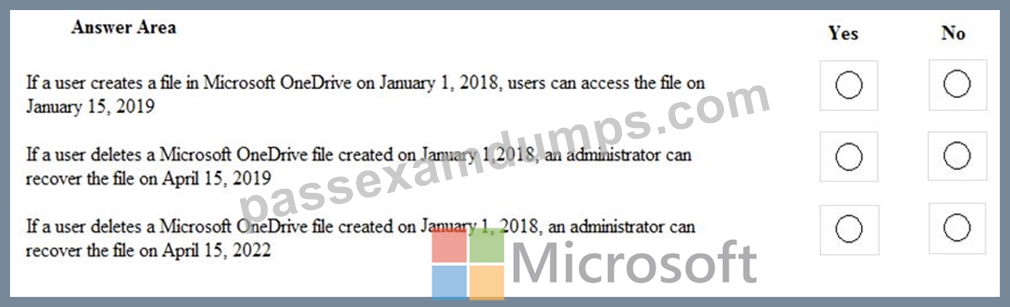
Answer:
Explanation: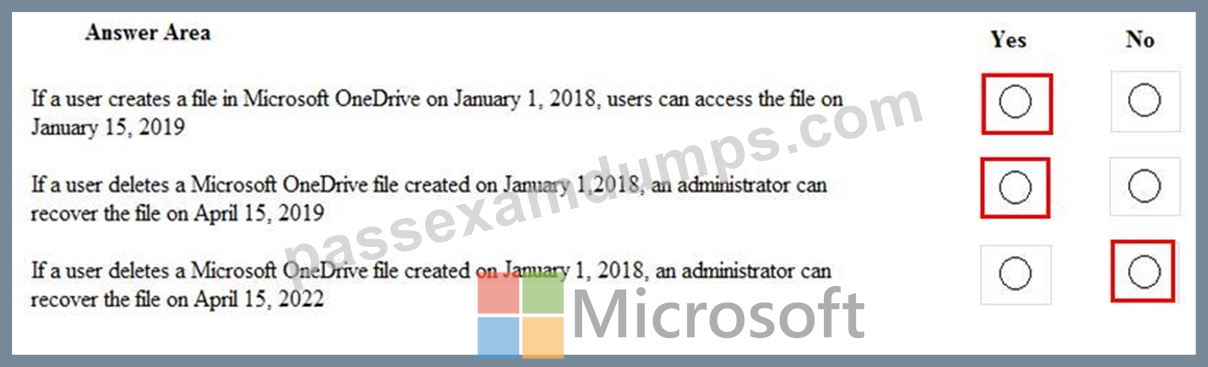
Reference:
https://docs.microsoft.com/en-us/office365/securitycompliance/retention-policies?redirectSourcePath=%252fen-us%252farticle%252fOverview-of-retention-policies-5e377752-700d-4870-9b6d-12bfc12d2423#the-principles-of-retention-or-what-takes-precedence
NEW QUESTION # 201
You have a Microsoft SharePoint Online sire named Site1 that contains the files shown in the following table.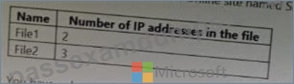
You have a data loss prevention (DLP) policy named DLP1 that has the advanced DLP rules shown in the following table.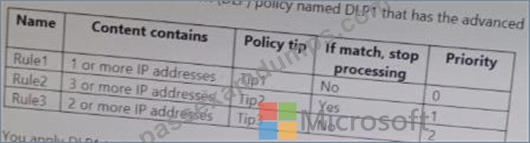
You apply DLP1 to Site1.
Which policy tips will appear for File2?
- A. Tip1 only
- B. Tip3 only
- C. Tip1 and Tip2 only
- D. Tip2 only
Answer: D
NEW QUESTION # 202
You have a Microsoft 365 Tenant.
A conditional access policy is configured for the tenant as shown in the Policy exhibit. (Click the Policy tab.)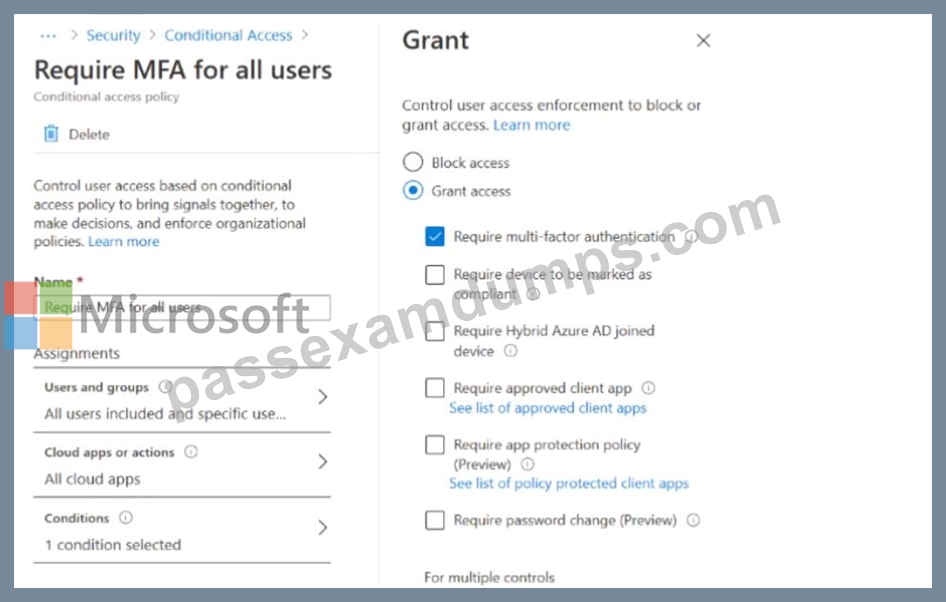
The User Administrator role a configured as shown in the Hole setting exhibit (Click the Role setting tab.)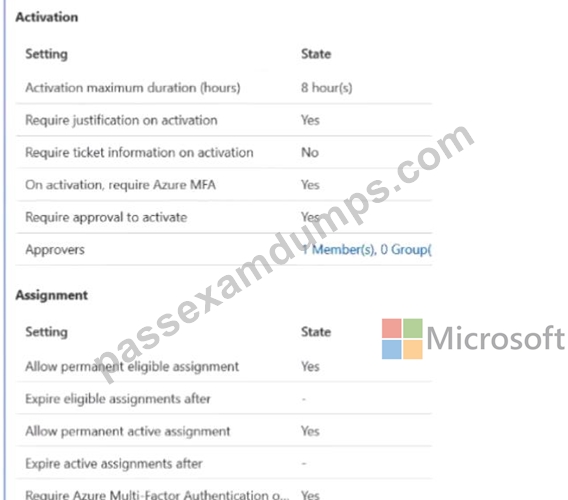
The User Administrator role has the assignments shown in the Assignments exhibit (Click the Assignments tab.)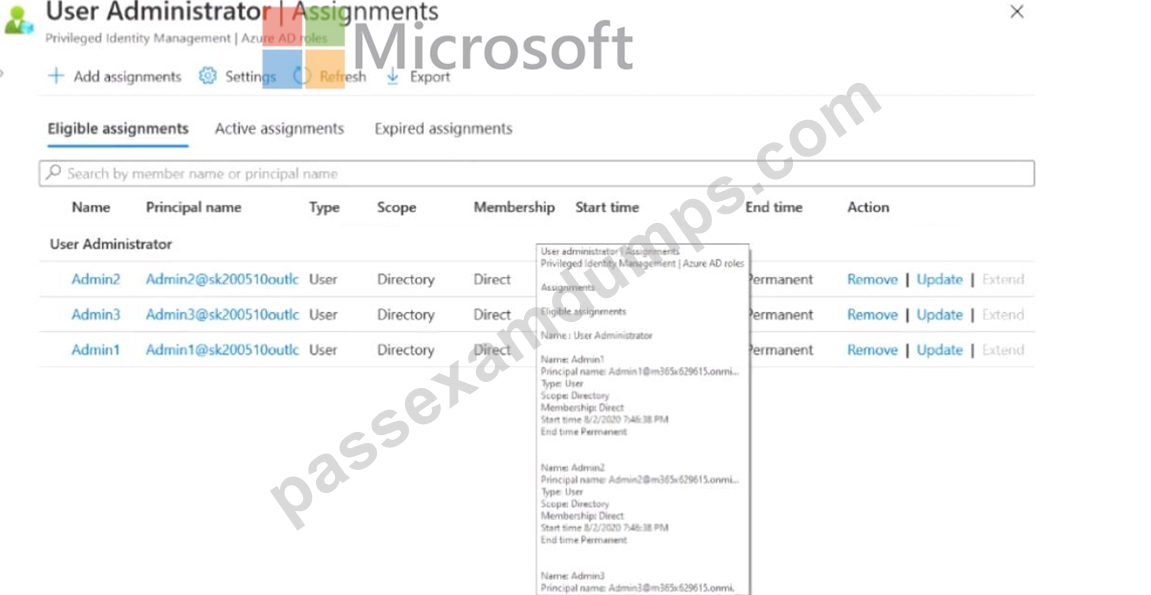
For each of the following statements, select yes If the statement is true. Otherwise select No.
NOTE Each correct selection is worth one point.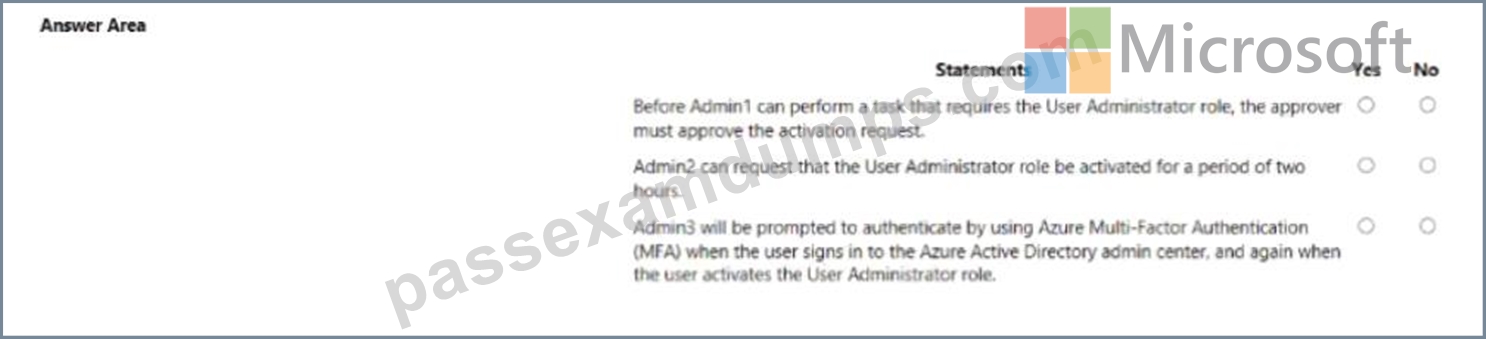
Answer:
Explanation: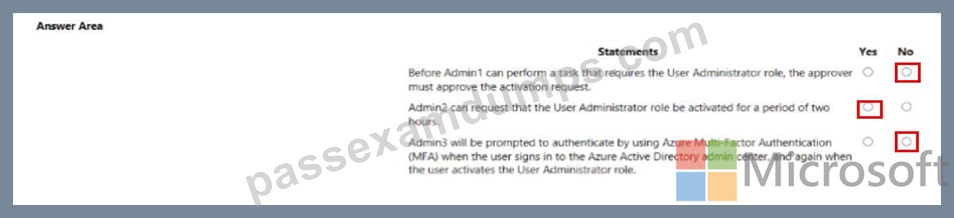
NEW QUESTION # 203
You have a Microsoft 365 subscription that contains the users shown in the following table.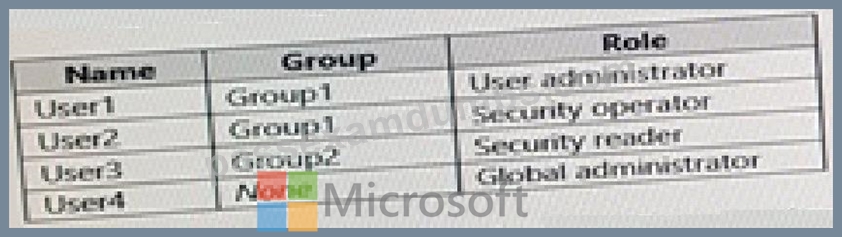
You enable self-service password reset for Group1 and configure security questions as the only authentication method for self-service password reset.
You need to identify which user must answer security questions to reset his password.
Which user should you identify?
- A. User1
- B. User2
- C. User4
- D. User3
Answer: B
NEW QUESTION # 204
You have a Microsoft 365 subscription. All users use Microsoft Exchange Online.
Microsoft 365 is configured to use the default policy settings without any custom rules.
You manage message hygiene.
Where are suspicious email messages placed by default? To answer, drag the appropriate location to the correct message types. Each location may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.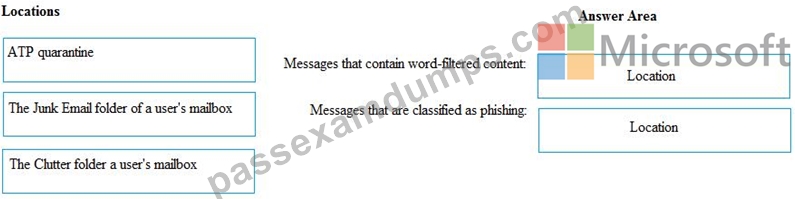
Answer:
Explanation: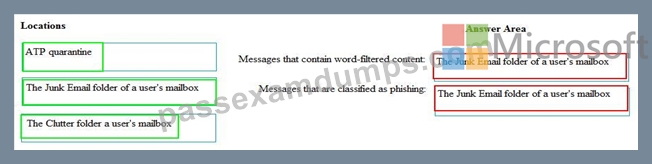
NEW QUESTION # 205
You have an Azure Active Directory (Azure AD) tenant named contoso.com that contains the users shown in the following table.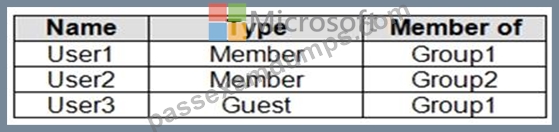
You assign an enterprise application named App1 to Group1 and User2.
You configure an Azure AD access review of App1. The review has the following settings:
Review name: Review1
Start date: 01-15-2020
Frequency: One time
End date: 02-14-2020
Users to review: Assigned to an application
Scope: Everyone
Applications: App1
Reviewers: Members (self)
Auto apply results to resource: Enable
Should reviewer not respond: Take recommendations
On February 15, 2020, you review the access review report and see the entries shown in the following table: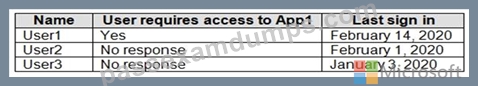
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.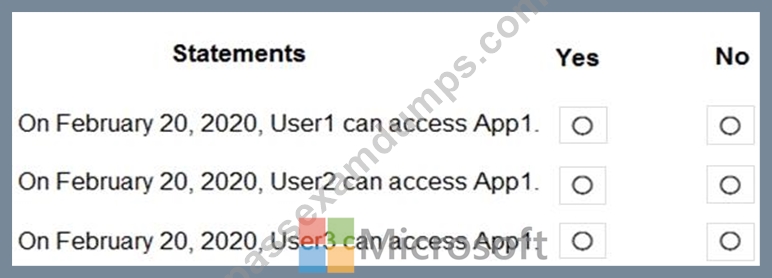
Answer:
Explanation: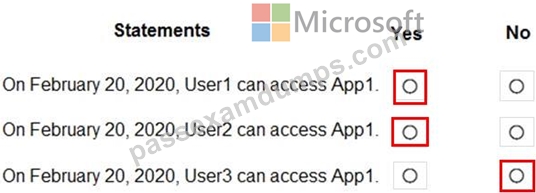
NEW QUESTION # 206
Your network contains an Active Directory domain named contoso.com. The domain contains a VPN server named VPN1 that runs Windows Server 2016 and has the Remote Access server role installed.
You have a Microsoft Azure subscription.
You are deploying Azure Advanced Threat Protection (ATP)
You install an Azure ATP standalone sensor on a server named Server1 that runs Windows Server 2016.
You need to integrate the VPN and Azure ATP.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.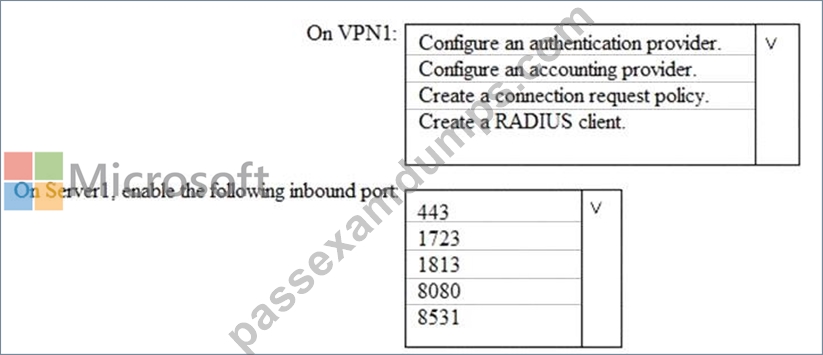
Answer:
Explanation: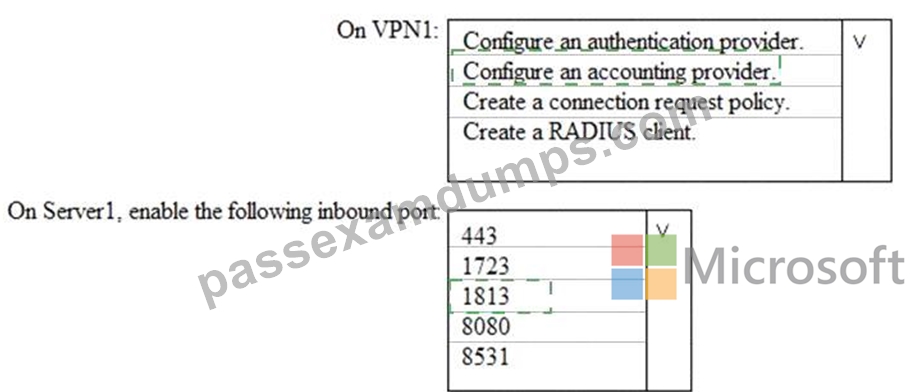
Explanation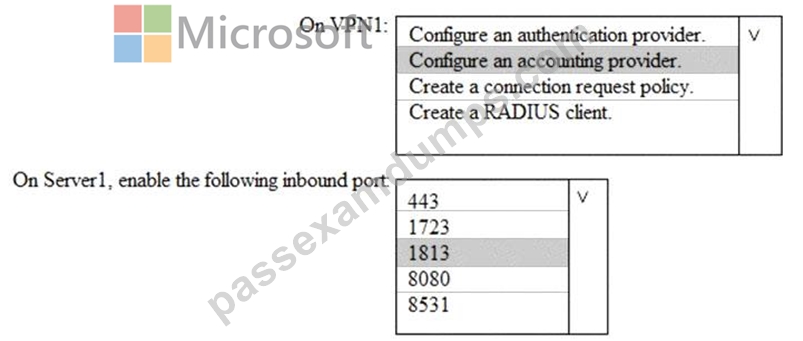
Reference:
https://docs.microsoft.com/en-us/azure-advanced-threat-protection/install-atp-step6-vpn
NEW QUESTION # 207
You have a Microsoft Azure Active Directory (Azure AD) tenant named contoso.com.
Four Windows 10 devices are joined to the tenant as shown in the following table.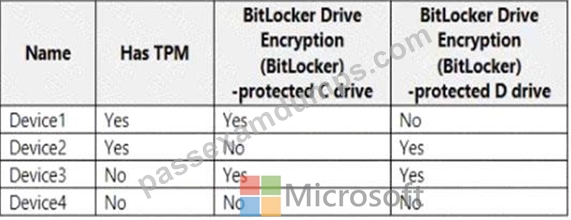
On which devices can you use BitLocker To Go and on which devices can you turn on auto-unlock? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.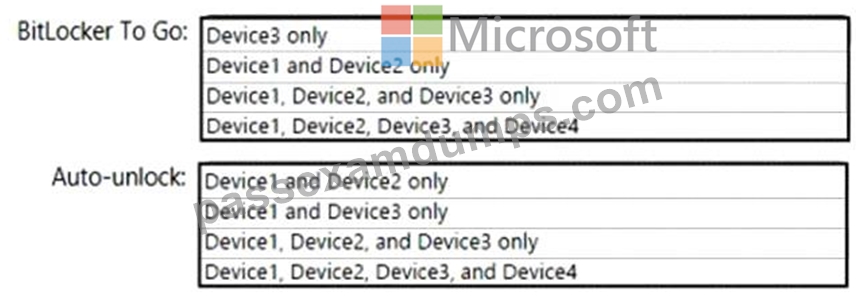
Answer:
Explanation: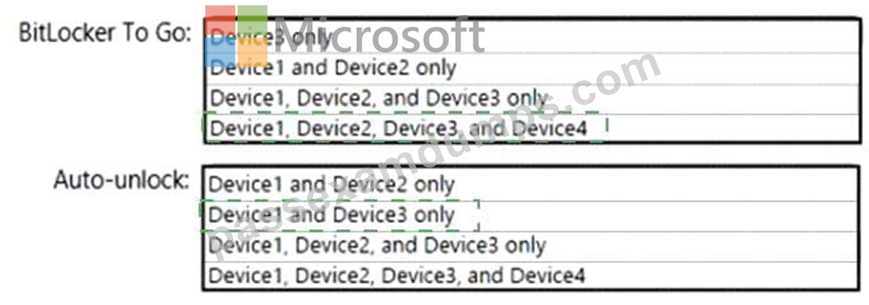
Explanation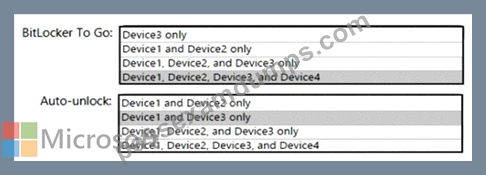
NEW QUESTION # 208
You have a Microsoft 365 subscription.
You identify the following data loss prevention (DLP) requirements:
* Send notifications to users if they attempt to send attachments that contain EU social security numbers
* Prevent any email messages that contain credit card numbers from being sent outside your organization
* Block the external sharing of Microsoft OneDrive content that contains EU passport numbers
* Send administrators email alerts if any rule matches occur.
What is the minimum number of DLP policies and rules you must create to meet the requirements? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.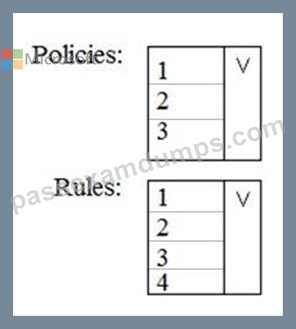
Answer:
Explanation: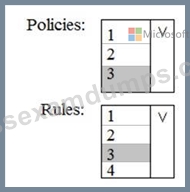
NEW QUESTION # 209
......
Updated MS-500 Dumps Questions For Microsoft Exam: https://www.passexamdumps.com/MS-500-valid-exam-dumps.html
Valid MS-500 Dumps for Helping Passing MS-500 Exam!: https://drive.google.com/open?id=1iqAXlFnUVxJ1Sv6FqOgdPjCq34bBIO13
