

CKS Practice Test Give You First Time Success with 100% Money Back Guarantee!
All Obstacles During CKS Exam Preparation with CKS Real Test Questions
NEW QUESTION # 27
SIMULATION
Create a User named john, create the CSR Request, fetch the certificate of the user after approving it.
Create a Role name john-role to list secrets, pods in namespace john
Finally, Create a RoleBinding named john-role-binding to attach the newly created role john-role to the user john in the namespace john. To Verify: Use the kubectl auth CLI command to verify the permissions.
Answer:
Explanation:
se kubectl to create a CSR and approve it.
Get the list of CSRs:
kubectl get csr
Approve the CSR:
kubectl certificate approve myuser
Get the certificate
Retrieve the certificate from the CSR:
kubectl get csr/myuser -o yaml
here are the role and role-binding to give john permission to create NEW_CRD resource:
kubectl apply -f roleBindingJohn.yaml --as=john
rolebinding.rbac.authorization.k8s.io/john_external-rosource-rb created kind: RoleBinding apiVersion: rbac.authorization.k8s.io/v1 metadata:
name: john_crd
namespace: development-john
subjects:
- kind: User
name: john
apiGroup: rbac.authorization.k8s.io
roleRef:
kind: ClusterRole
name: crd-creation
kind: ClusterRole
apiVersion: rbac.authorization.k8s.io/v1
metadata:
name: crd-creation
rules:
- apiGroups: ["kubernetes-client.io/v1"]
resources: ["NEW_CRD"]
verbs: ["create, list, get"]
NEW QUESTION # 28
You need to configure a Kubernetes cluster to use a pod security policy (PSP) that restricts the use of privileged containers and specific capabilities. You want to only allow specific pods in the 'production' namespace to run With the 'NET_ADMIN' capability.
Answer:
Explanation:
Solution (Step by Step) :
1. create a PSPI
- Define a PSP that restricts the use of privileged containers and capabilities, except for the capability for pods in the 'production' namespace.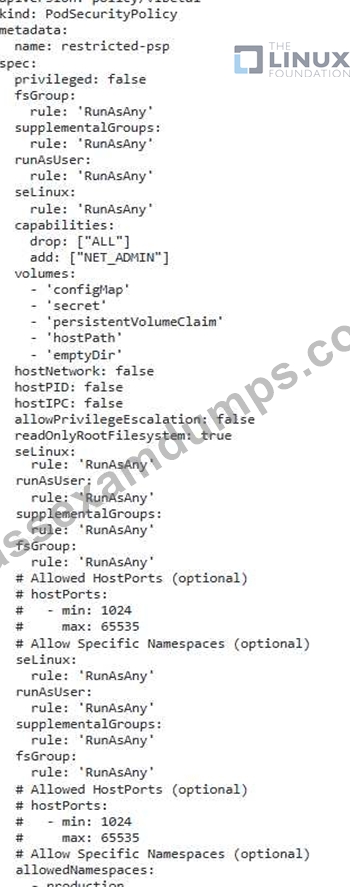
2. Create a PSP Binding: - Bind the PSP to the 'production' namespace-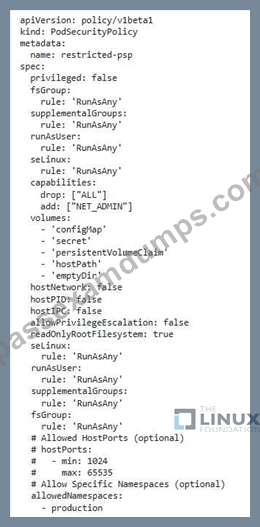
3. Create a Pod: - Create a Pod in the 'production' namespace and specify the 'securitycontext' with the 'NET_ADMIN' capability.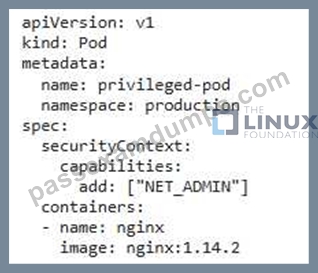
4. Apply the YAML files: - Apply the created YAML files using 'kubectl apply -f 5. Verify the permissions: - Try to create a Pod in other namespaces with the 'NET_ADMIN' capability. It should be rejected.
NEW QUESTION # 29
You are running a multi-tenant Kubernetes cluster where different teams deploy their applications. You are tasked with ensuring isolation between teams and preventing unauthorized access to sensitive dat
a. Describe how you can leverage pod security policies (PSP) and network policies to achieve this goal.
Answer:
Explanation:
Solution (Step by Step):
1. Define Pod Security Policies:
- Create separate PSPs for each team with different security constraints:
- Resource Limits: Limit the resources each team's pods can request (CPU, memory).
- Capabilities: Restrict specific capabilities like ' SYS_ADMIN' or 'NET_ADMIN'
- Security Context: Control the user and group IDs, privileged escalation, and SELinux labels for pods.
- Volume Types: Allow only specific types of volumes (e.g., emptyDir, hostPath, persistentV01umeClaim).
- Example PSP for Team A: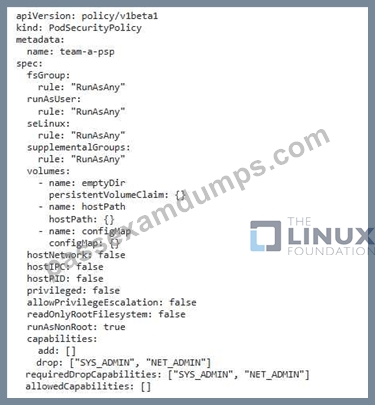
2. Apply PSPs to Teams: - Use 'kubectl apply -f team-a-psp.yaml' to apply the PSP for Team A. - Create and apply similar PSPs for other teams. - Apply these PSPs as admission controllers in your cluster to enforce them on all pods. 3. Configure Network Policies: - Define network policies to control communication between pods within different teams: - Ingress Policy: Control whicn pods can initiate connections to pods in otner teams. - Egress Policy: Control which pods can receive connections from pods in other teams. - Example Network Policy for Team A: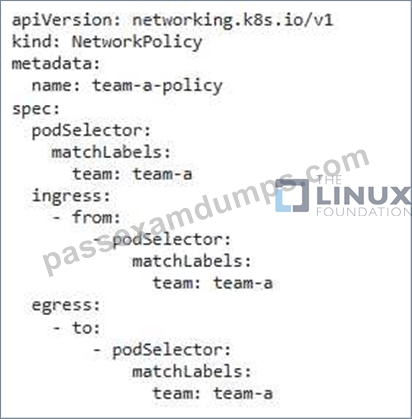
4. Apply Network Policies: - Use ' kubectl apply -f team-a-policy-yamp to apply the policy for Team A. - Create and apply similar policies for other teams. Result: - These PSPs and network policies enforce isolation between teams, limiting their access to resources and preventing unauthorized communication. - Teams can deploy their applications within their defined policies, minimizing the risk of cross-team vulnerabilities. - This approach ensures a secure and isolated environment for multi-tenant deployments.
NEW QUESTION # 30
You are running a Kubernetes cluster with a deployment named "my-app" that uses a container image from a public registry. The container image has a vulnerability in a library it uses. You want to apply a security patch to the container image without rebuilding it. Explain how you would implement this using a container patching tool like 'image-patcners and update the deployment.
Answer:
Explanation:
Solution (Step by Step) :
1. Install 'image-patchers:
- Install the 'image-patcher' tool on your system or within your Kubernetes cluster. 'image-patcher' is a tool for patching container images without rebuilding thenm It allows you to modify the container image's filesystem and update libraries directly.
2. Identify the Vulnerable Library:
- Use a vulnerability scanner like Trivy to identify the specific vulnerable library within the container image.
3. Patch the Vulnerable Library:
- Use 'image-patcher' to apply the security patch to the vulnerable library within the container image.
- You can use the 'image-patcher apply' command with the patch file and tne container image name to apply the patch.
4. Create a Patched Image:
- 'image-patcher' Will generate a new, patched container image. This patched image will contain the updated library with the security fix applied.
5. Push the Patched Image to a Registry:
- Push the patched image to your private container registry for use in deployments.
6. Update the Deployment
- Update the "my-app" deployment configuration to use the newly created patched image from your private registry.
7. Validate the Patch:
- After updating the deployment, verify that the patch has been successfully applied by running a vulnerability scan on the running container.
NEW QUESTION # 31
On the Cluster worker node, enforce the prepared AppArmor profile
#include <tunables/global>
profile nginx-deny flags=(attach_disconnected) {
#include <abstractions/base>
file,
# Deny all file writes.
deny /** w,
}
EOF'
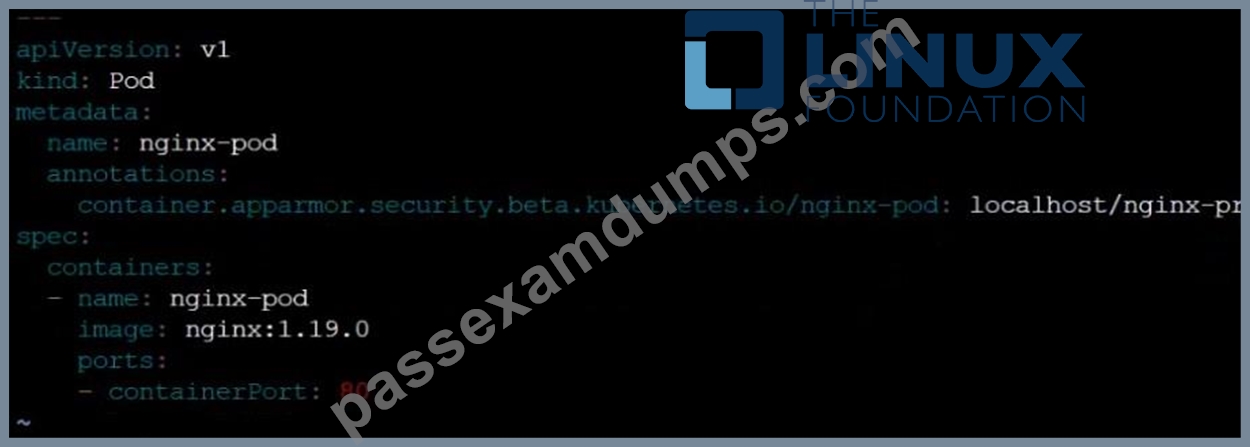
Edit the prepared manifest file to include the AppArmor profile.
apiVersion: v1
kind: Pod
metadata:
name: apparmor-pod
spec:
containers:
- name: apparmor-pod
image: nginx
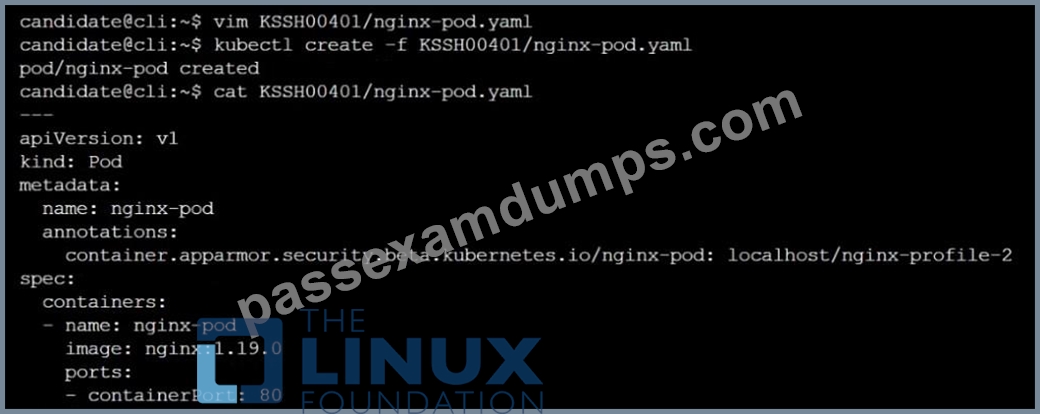
Finally, apply the manifests files and create the Pod specified on it.
Verify: Try to make a file inside the directory which is restricted.
Answer:
Explanation: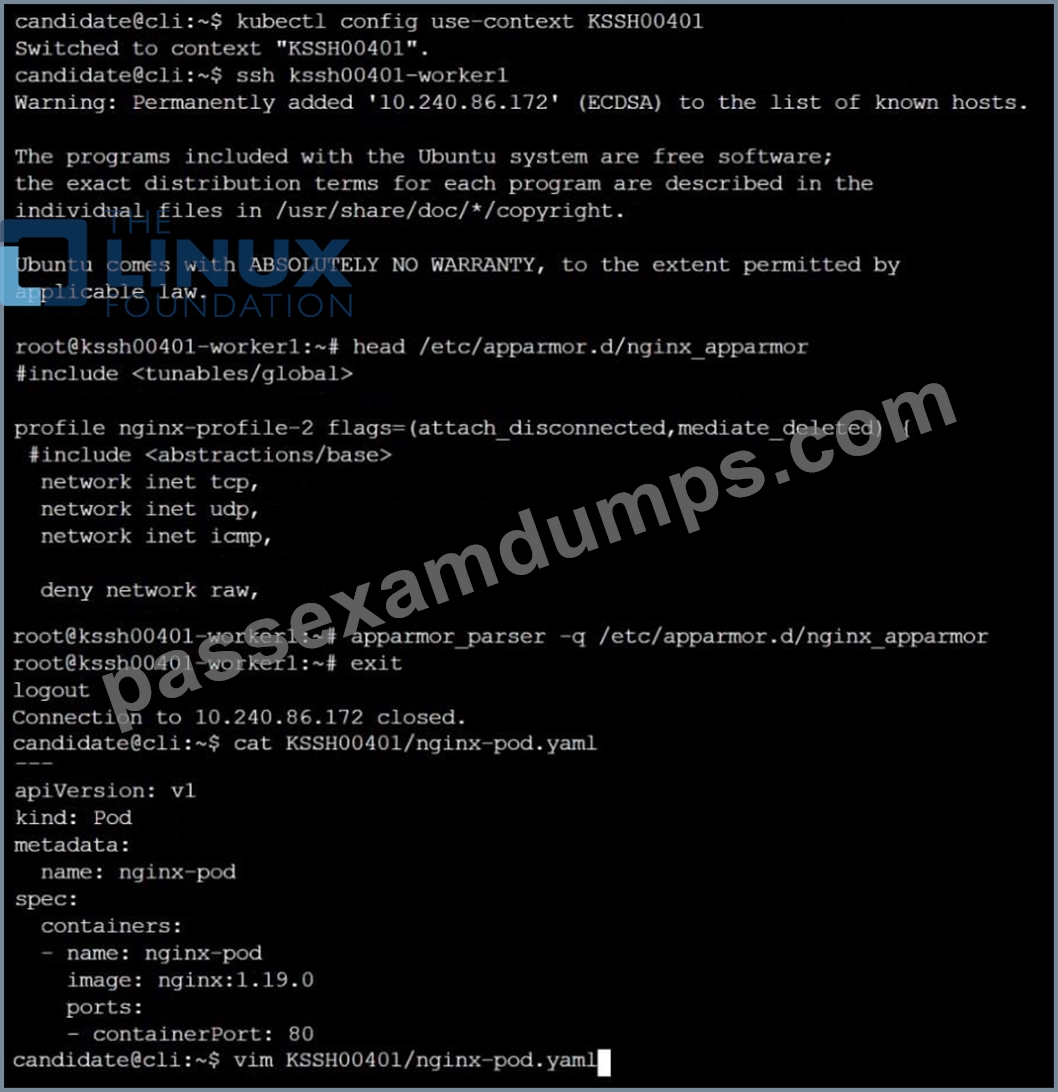
NEW QUESTION # 32
You have a Kubernetes cluster running an application with multiple deployments. You want to implement RBAC rules to ensure that only specific users can manage the deployments belonging to their respective teams. For instance, the "dev" team should only be able to manage deployments With the label 'team: dev' , while the "ops" team should only manage deployments With the label steam: 'ops'.
Answer:
Explanation:
Solution (Step by Step) :
1. Create Role for Each Team:
- dev-role.yaml: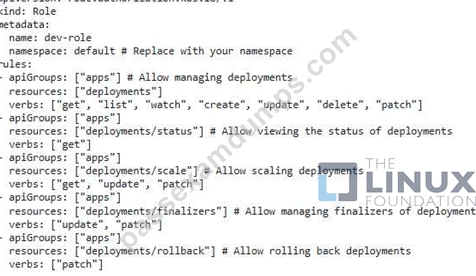
- ops-role_yaml: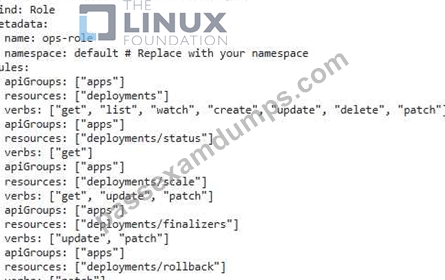
2. Create RoleBindings for Each Team: - dev-rolebinding.yaml: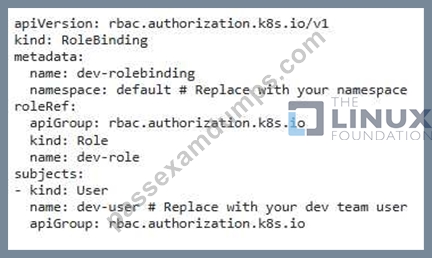
- ops-rolebinding.yaml: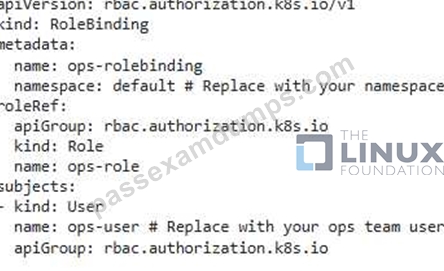
3. Apply the Roles and RoleBindings: - Apply the YAML files using kubectl apply -f dev-role.yaml dev-rolebinding.yaml ops-role.yaml ops-rolebinding.yamr 4. Create Test Deployments (with Team Labels): - Create a deployment labeled with steam: devs and another labeled with 'team: ops'. You can use 'kubectl create deployment with the appropriate label. 5. Verify RBAC Permissions: - Log in as the "dev" user and attempt to manage the "dev" team deployment. - Log in as the "ops" user and attempt to manage the "ops" team deployment - The users should only be able to access the deployments belonging to their respective teams.
NEW QUESTION # 33
SIMULATION
On the Cluster worker node, enforce the prepared AppArmor profile
#include <tunables/global>
profile docker-nginx flags=(attach_disconnected,mediate_deleted) {
#include <abstractions/base>
network inet tcp,
network inet udp,
network inet icmp,
deny network raw,
deny network packet,
file,
umount,
deny /bin/** wl,
deny /boot/** wl,
deny /dev/** wl,
deny /etc/** wl,
deny /home/** wl,
deny /lib/** wl,
deny /lib64/** wl,
deny /media/** wl,
deny /mnt/** wl,
deny /opt/** wl,
deny /proc/** wl,
deny /root/** wl,
deny /sbin/** wl,
deny /srv/** wl,
deny /tmp/** wl,
deny /sys/** wl,
deny /usr/** wl,
audit /** w,
/var/run/nginx.pid w,
/usr/sbin/nginx ix,
deny /bin/dash mrwklx,
deny /bin/sh mrwklx,
deny /usr/bin/top mrwklx,
capability chown,
capability dac_override,
capability setuid,
capability setgid,
capability net_bind_service,
deny @{PROC}/* w, # deny write for all files directly in /proc (not in a subdir)
# deny write to files not in /proc/<number>/** or /proc/sys/**
deny @{PROC}/{[^1-9],[^1-9][^0-9],[^1-9s][^0-9y][^0-9s],[^1-9][^0-9][^0-9][^0-9]*}/** w, deny @{PROC}/sys/[^k]** w, # deny /proc/sys except /proc/sys/k* (effectively /proc/sys/kernel) deny @{PROC}/sys/kernel/{?,??,[^s][^h][^m]**} w, # deny everything except shm* in /proc/sys/kernel/ deny @{PROC}/sysrq-trigger rwklx, deny @{PROC}/mem rwklx, deny @{PROC}/kmem rwklx, deny @{PROC}/kcore rwklx, deny mount, deny /sys/[^f]*/** wklx, deny /sys/f[^s]*/** wklx, deny /sys/fs/[^c]*/** wklx, deny /sys/fs/c[^g]*/** wklx, deny /sys/fs/cg[^r]*/** wklx, deny /sys/firmware/** rwklx, deny /sys/kernel/security/** rwklx,
}
Edit the prepared manifest file to include the AppArmor profile.
apiVersion: v1
kind: Pod
metadata:
name: apparmor-pod
spec:
containers:
- name: apparmor-pod
image: nginx
Finally, apply the manifests files and create the Pod specified on it.
Verify: Try to use command ping, top, sh
- A. Send us the Feedback on it.
Answer: A
NEW QUESTION # 34
Analyze and edit the given Dockerfile
FROM ubuntu:latest
RUN apt-get update -y
RUN apt-install nginx -y
COPY entrypoint.sh /
ENTRYPOINT ["/entrypoint.sh"]
USER ROOT
Fixing two instructions present in the file being prominent security best practice issues Analyze and edit the deployment manifest file apiVersion: v1 kind: Pod metadata:
name: security-context-demo-2
spec:
securityContext:
runAsUser: 1000
containers:
- name: sec-ctx-demo-2
image: gcr.io/google-samples/node-hello:1.0
securityContext:
runAsUser: 0
privileged: True
allowPrivilegeEscalation: false
Fixing two fields present in the file being prominent security best practice issues Don't add or remove configuration settings; only modify the existing configuration settings Whenever you need an unprivileged user for any of the tasks, use user test-user with the user id 5487
- A. Send us your Feedback on this.
Answer: A
NEW QUESTION # 35
Before Making any changes build the Dockerfile with tag base:v1
Now Analyze and edit the given Dockerfile(based on ubuntu 16:04)
Fixing two instructions present in the file, Check from Security Aspect and Reduce Size point of view.
Dockerfile:
FROM ubuntu:latest
RUN apt-get update -y
RUN apt install nginx -y
COPY entrypoint.sh /
RUN useradd ubuntu
ENTRYPOINT ["/entrypoint.sh"]
USER ubuntu
entrypoint.sh
#!/bin/bash
echo "Hello from CKS"
After fixing the Dockerfile, build the docker-image with the tag base:v2
- A. To Verify: Check the size of the image before and after the build.
Answer: A
NEW QUESTION # 36
You are running a multi-tenant Kubernetes cluster where different teams manage their own applications. You want to ensure that each team's applications are isolated from each other to prevent potential security risks.
How would you use Network Policies to achieve this isolation?
Answer:
Explanation:
Solution (Step by Step) :
1. Create separate namespaces for each team: This is the foundation for network isolation.
2. Define Network Policies for each namespace:
Restrict inbound traffic: Only allow specific protocols and ports from trusted sources to access the namespace.
Control outbound traffic: Limit outbound connections from pods within the namespace to specific destinations.
Example Network Policy (ingress):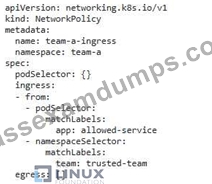
3. Apply the Network Policies: bash kubectl apply -f team-a-ingress-yaml kubectl apply -f team-b-ingress.yaml # Apply policies for other namespaces Example Scenario: Team A: Runs a web application accessible only from within its namespace. Team B: Runs a database service that can be accessed by Team A's application but not by other teams. Network Policies: Team A Network Policy: Ingress: Only allow traffic from Team B's database service- Egress Allow outbound traffic to the internet for updates and dependencies. Team B Network Policy: Ingress: Allow traffic from Team A's web application Egress Limit outbound traffic to specific servers for backups and maintenance. Note: Network Policies are a powerful tool for achieving network isolation in Kubernetes. They allow you to fine-tune the communication patterns between pods and namespaces, enhancing security and mitigating potential risks.
NEW QUESTION # 37
SIMULATION
Documentation Upgrading kubeadm clusters
You must connect to the correct host . Failure to do so may result in a zero score.
[candidate@base] $ ssh cks000034
Context
The kubeadm provisioned cluster was recently upgraded, leaving one node on a slightly older version due to workload compatibility concerns.
Task
Upgrade the cluster node compute-0 to match the version of the control plane node.
Use a command like the following to connect to the compute node:
[candidate@cks000034] $ ssh compute-0
Do not modify any running workloads in the cluster.
Do not forget to exit from the compute node once you have completed your tasks:
[candidate@icompute-e] $ exit
Answer:
Explanation:
See the Explanation below for complete solution
Explanation:
Below is the CKS / CKA exam-style, exact step-by-step solution for Upgrading a kubeadm worker node.
Follow in order, type exact commands, no extra actions.
QUESTION - Upgrade node compute-0 (EXAM MODE)
1) Connect to the correct host (control plane)
ssh cks000034
sudo -i
export KUBECONFIG=/etc/kubernetes/admin.conf
2) Identify the control plane Kubernetes version
This is the target version for compute-0.
kubectl get nodes
Example output:
NAME STATUS ROLES VERSION
control-plane Ready control-plane v1.27.4
compute-0 Ready <none> v1.26.6
Note the control-plane version
Example: v1.27.4
3) Drain the compute node (do NOT modify workloads manually)
kubectl drain compute-0 --ignore-daemonsets --delete-emptydir-data
Wait until drain completes successfully.
4) SSH into the compute node
ssh compute-0
sudo -i
5) Check current kubeadm version on compute node
kubeadm version
6) Upgrade kubeadm to match control plane version
Replace 1.27.4 with the exact control-plane version you observed.
apt-get update
apt-get install -y kubeadm=1.27.4-00
Verify:
kubeadm version
7) Run kubeadm upgrade for the node
kubeadm upgrade node
✅ This updates node-specific configs (NO workloads touched).
8) Upgrade kubelet and kubectl to the same version
apt-get install -y kubelet=1.27.4-00 kubectl=1.27.4-00
9) Restart kubelet
systemctl daemon-reload
systemctl restart kubelet
systemctl status kubelet --no-pager
10) Exit the compute node (IMPORTANT)
exit
11) Uncordon the compute node (back on control plane)
kubectl uncordon compute-0
12) Final verification
kubectl get nodes
Expected:
NAME STATUS VERSION
compute-0 Ready v1.27.4
NEW QUESTION # 38
You are deploying a new microservice to your Kubernetes cluster. This microservice will handle sensitive user data and requires access to a database that is also deployed on the cluster. To ensure secure communication between the microservice and the database, you need to configure mutual TLS authentication.
Explain the steps involved in setting up mutual TLS authentication between the microservice and the database.
Answer:
Explanation:
Solution (Step by Step) :
1. Generate Certificates:
- Create a Certificate Authority (CA) to issue certificates for the microservice and the database.
- Generate a self-signed certificate and key for the CA.
- Example (using OpenSSL):
bash
openssl genrsa -out cakey 2048
openssl req -new -x509 -key ca.key -out ca.crt -days 365 -subj Francisco/O=My Company/OU=lT Department/CN=myCA"
2. Generate Certificates for the Microservice and Database:
- Use the CA certificate and key to sign certificates for tne microservice and the database.
- Example (using OpenSSL):
bash
# Generate a certificate request for the microservice
openssl req -new -key microservice-key -out microservice-csr -subj "/C=US/ST=California/L=San Francisco,'O=My Company/OU=lT
Department/CN=microservice"
# Sign the certificate request with the CA
openssl x509 -req -in microservice.csr -CA ca.crt -CAkey ca.key -out microservice-crt -days 365
# Repeat for the database
3. Create Kubernetes Secrets:
- Create secrets in the cluster to store the certificates and keys for the microservice and database.
- Example: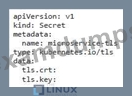
4. Configure the Microservice Container: - Update tne microservice deployment YAML to mount the certificate and key secret. - Set the 'TLS parameters in the database connection string. - Example: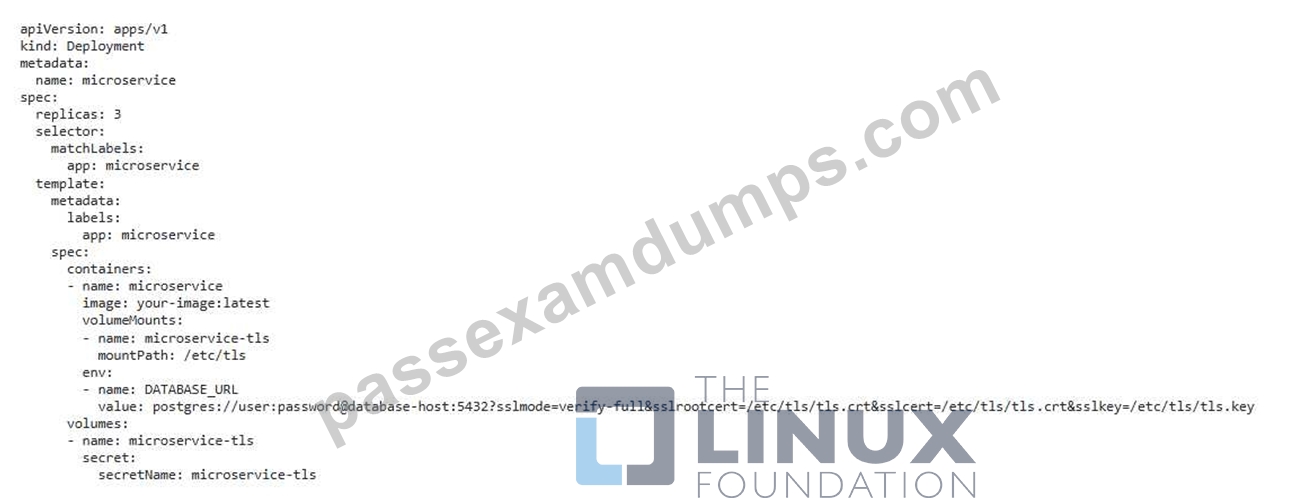
5. Configure the Database Container: - Repeat the steps for the database container, using the database certificate and key. 6. Verify Communication: - Ensure that the microservice can connect to the database securely using mutual TLS authentication. - Test the application to ensure that it functions correctly. These are just a few examples of how to create and utilize custom base images, network policies, RBAC, and mutual TLS- Implementing robust security in Kubernetes is an ongoing effort that requires continuous monitoring and updates to mitigate potential threats.
NEW QUESTION # 39
You are responsible for managing the software supply chain of a critical application deployed in a Kubernetes cluster. This application utilizes a library called 'lib-crypto' for secure cryptographic operations. How can you ensure that the version of 'lib-ctypto' deployed in your Kubernetes environment is the same as the one specified in the Software Bill of Materials (SBOM) for the application?
Answer:
Explanation:
Solution (Step by Step) :
1. Obtain the SBOM: Retrieve the SBOM for your application. This document will contain a list of all the components and their versions, including 'lib- crypto'. The SBOM can be generated using various tools like 'cyclonedx-boms or 'Sbom-cli'.
2. Parse the S80M: IJse a suitable tool or script to parse the SdOM and extract the version of 'lib-crypto' from the S80M_
3. Verify in the Deployment Manifest: Inspect the deployment manifest for your application. Look for the container definition that uses the 'lib-crypto' image. Ensure that the image tag used in the deployment manifest matches the version of 'Iib-crypto' extracted from the SBOM_
4. Implement Image Scanning: Integrate an image scanning tool like 'Clair' or 'Anchores into your CI/CD pipeline. This will scan the 'Iib-crypto' image before deployment to ensure it doesn't contain any vulnerabilities or unexpected components.
5. Use a Container Registry with SBOM Support: Consider using a container registry like JFrog Xray or Snyk Container which supports storing and verifying S80Ms for each image. This provides a centralized mechanism for tracking and validating the software components in your container images.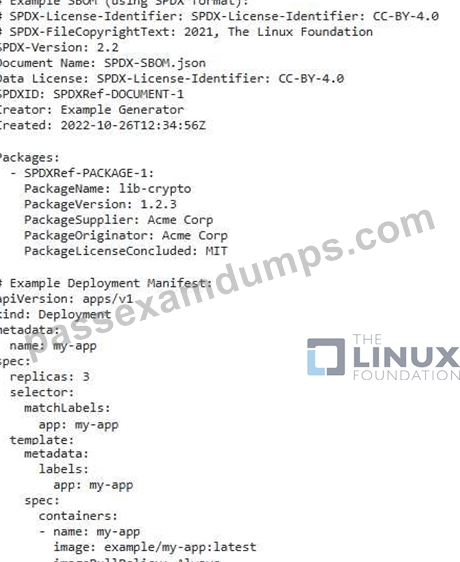
NEW QUESTION # 40
You are running a Kubernetes cluster that hosts a critical database application. You need to implement a policy that prevents any unauthorized access to the database pod from other pods within the cluster.
Answer:
Explanation:
Solution (Step by Step) :
1. Create a Network Policy:
- Create a NetworkPolicy in the namespace of your database pod: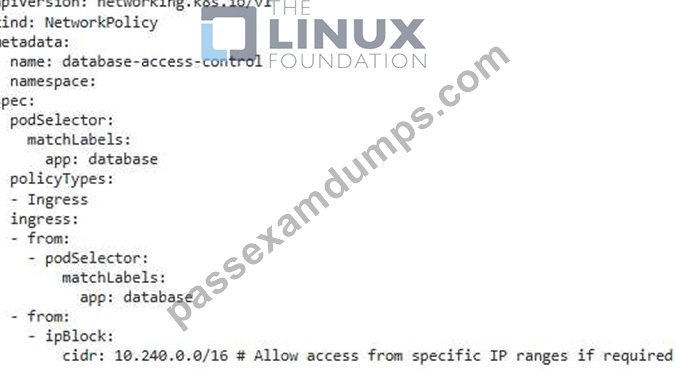
2. Apply the Network Policy: - Apply the NetworkP01iCY using 'kubectl apply -f database-access-control.yaml 3. Test the Policy: - Run a pod in a different namespace or with a different label and attempt to connect to the database pod. - The NetworkPolicy should prevent any unauthorized access.
NEW QUESTION # 41
You have a Kubernetes cluster running a highly sensitive application. You need to ensure that the application's data is encrypted at rest and in transit. What security measures would you implement to achieve this?
Answer:
Explanation:
Solution (Step by Step):
Data Encryption at Rest:
1. Volume Encryption:
- Kubernetes Persistent Volumes (PVs): Use volume encryption on the underlying storage system (e.g., EBS, GCE PD) to encrypt data at rest. This ensures tnat the data stored in the PV is encrypted even if tne underlying volume iS stolen or accessed Without authorization.
- Container Storage Interface (CSI): If using CSI drivers, utilize their volume encryption capabilities (if supported) to encrypt data on the storage volume.
2. Secret Encryptiom
- Kubernetes Secrets: Encrypt sensitive data stored in Secrets using tools like HashiCorp Vault, AWS KMS, or Google Cloud KMS. This prevents unauthorized access to sensitive information like API keys, passwords, and certificates.
Data Encryption in Transit:
1. TLS/SSL:
- Network Communication: Encrypt all network communication using TLS/SSL between pods, services, and external applications. This prevents eavesdropping and data interception.
- Service Mesn: Utilize a service mesh like Istio or Linkerd that automatically enforces TLS/SSL for inter-pod communication. This Simplifies the configuration and management of TLS.
2. Network Policy:
- Restrict Network Access: Implement NetworkPolicy to restrict inbound and outbound traffic to the pods running the sensitive application. This minimizes the attack surface and prevents unauthorized access to the application's network interfaces.
Additional Security Measures:
1. Pod Security Policies (PSP): Use PSPs to restrict the capabilities of pods running the sensitive application. This limits the potential for unauthorized access to the host system or other resources.
2. Security Context: Use the 'securitycontext field for pods to control their security settings. For example, you can set the 'runAslJser' and
'runAsGroups to ensure that the pod runs as a non-root user.
Example Configuration: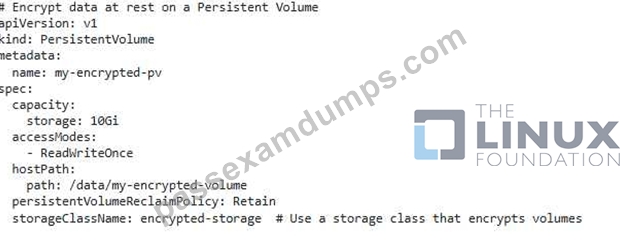
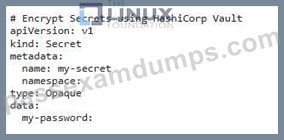
Important Notes: - Choose the appropriate encryption solutions based on your cluster environment and security requirements. - Ensure the key management strategy is secure and compliant with your organization's policies. - Regularly audit and review security configurations to maintain a strong security posture.
NEW QUESTION # 42
You are tasked with ensuring the security of a Kubernetes cluster running a sensitive application. Describe now you would implement a "least privilege" principle for both users and service accounts in this cluster.
Answer:
Explanation:
Solution (Step by Step) :
1. User Roles and Permissions:
- Define specific roles with minimal permissions for different user groups based on their responsibilities.
- For example, developers might have access to deploy applications, while operations team members might have access to manage resources.
- use RBAC (Role-Based Access Control) in Kubemetes to define roles and assign them to users.
2. Service Account Permissions:
- Create separate service accounts for each application or service in the cluster.
- Grant the service accounts only the necessary permissions to perform their specific tasks.
- Avoid using default service accounts with broad permissions.
- Employ the "principle ot least privilege" by defining minimal permissions for service accounts.
3. Pod Security Policies (PSPs):
- Implement PSPs to enforce security constraints on pods, restricting resources that they can access.
- Define PSPs to allow only specific container images, disable privileged containers, limit resource requests, and enforce other security controls.
- Consider using Pod Security Admission (PSA) as a replacement for PSPs in Kubernetes 1.25+.
4. Network Policies:
- Implement network policies to control network communication between pods and services.
- Define rules that allow only necessary traffic between pods, restricting any unnecessary or unauthorized connections.
5. Secret Management
- Utilize Kubernetes Secrets to store sensitive information like passwords and API keys.
- Limit access to secrets based on the principle of least privilege.
- Avoid storing sensitive information directly in deployment YAML files.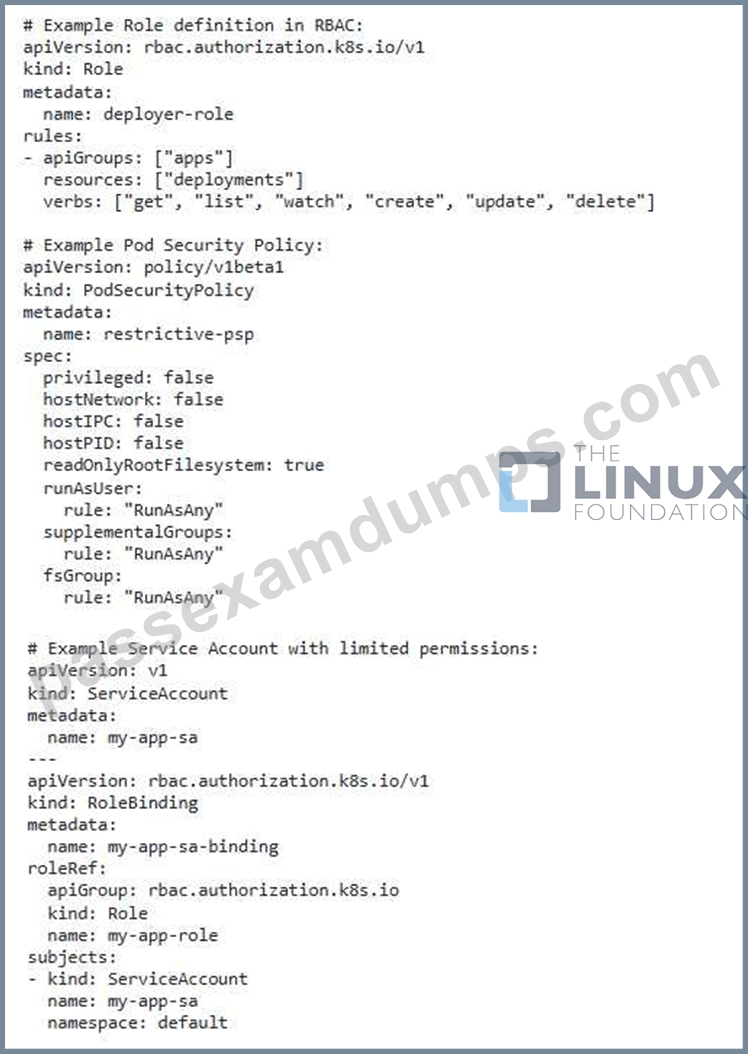
NEW QUESTION # 43
SIMULATION
You can switch the cluster/configuration context using the following command:
[desk@cli] $ kubectl config use-context dev
Context:
A CIS Benchmark tool was run against the kubeadm created cluster and found multiple issues that must be addressed.
Task:
Fix all issues via configuration and restart the affected components to ensure the new settings take effect.
Fix all of the following violations that were found against the API server:
1.2.7 authorization-mode argument is not set to AlwaysAllow FAIL
1.2.8 authorization-mode argument includes Node FAIL
1.2.7 authorization-mode argument includes RBAC FAIL
Fix all of the following violations that were found against the Kubelet:
4.2.1 Ensure that the anonymous-auth argument is set to false FAIL
4.2.2 authorization-mode argument is not set to AlwaysAllow FAIL (Use Webhook autumn/authz where possible) Fix all of the following violations that were found against etcd:
2.2 Ensure that the client-cert-auth argument is set to true
Answer:
Explanation:
See the Explanation below
Explanation:
worker1 $ vim /var/lib/kubelet/config.yaml
anonymous:
enabled: true #Delete this
enabled: false #Replace by this
authorization:
mode: AlwaysAllow #Delete this
mode: Webhook #Replace by this
worker1 $ systemctl restart kubelet. # To reload kubelet config
ssh to master1
master1 $ vim /etc/kubernetes/manifests/kube-apiserver.yaml
- -- authorization-mode=Node,RBAC
master1 $ vim /etc/kubernetes/manifests/etcd.yaml
- --client-cert-auth=true
Explanation:
ssh to worker1
worker1 $ vim /var/lib/kubelet/config.yaml
apiVersion: kubelet.config.k8s.io/v1beta1
authentication:
anonymous:
enabled: true #Delete this
enabled: false #Replace by this
webhook:
cacheTTL: 0s
enabled: true
x509:
clientCAFile: /etc/kubernetes/pki/ca.crt
authorization:
mode: AlwaysAllow #Delete this
mode: Webhook #Replace by this
webhook:
cacheAuthorizedTTL: 0s
cacheUnauthorizedTTL: 0s
cgroupDriver: systemd
clusterDNS:
- 10.96.0.10
clusterDomain: cluster.local
cpuManagerReconcilePeriod: 0s
evictionPressureTransitionPeriod: 0s
fileCheckFrequency: 0s
healthzBindAddress: 127.0.0.1
healthzPort: 10248
httpCheckFrequency: 0s
imageMinimumGCAge: 0s
kind: KubeletConfiguration
logging: {}
nodeStatusReportFrequency: 0s
nodeStatusUpdateFrequency: 0s
resolvConf: /run/systemd/resolve/resolv.conf
rotateCertificates: true
runtimeRequestTimeout: 0s
staticPodPath: /etc/kubernetes/manifests
streamingConnectionIdleTimeout: 0s
syncFrequency: 0s
volumeStatsAggPeriod: 0s
worker1 $ systemctl restart kubelet. # To reload kubelet config
ssh to master1
master1 $ vim /etc/kubernetes/manifests/kube-apiserver.yaml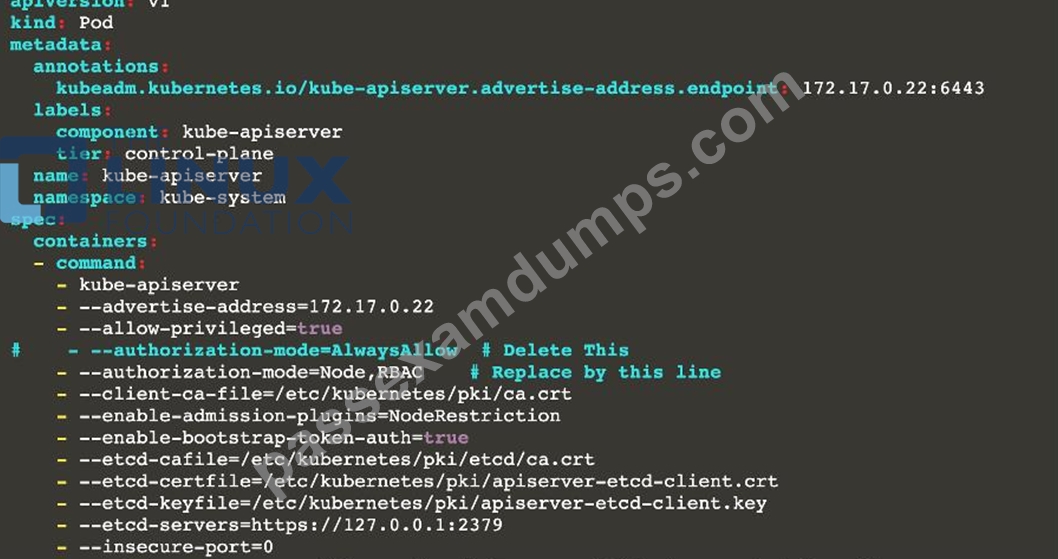
master1 $ vim /etc/kubernetes/manifests/etcd.yaml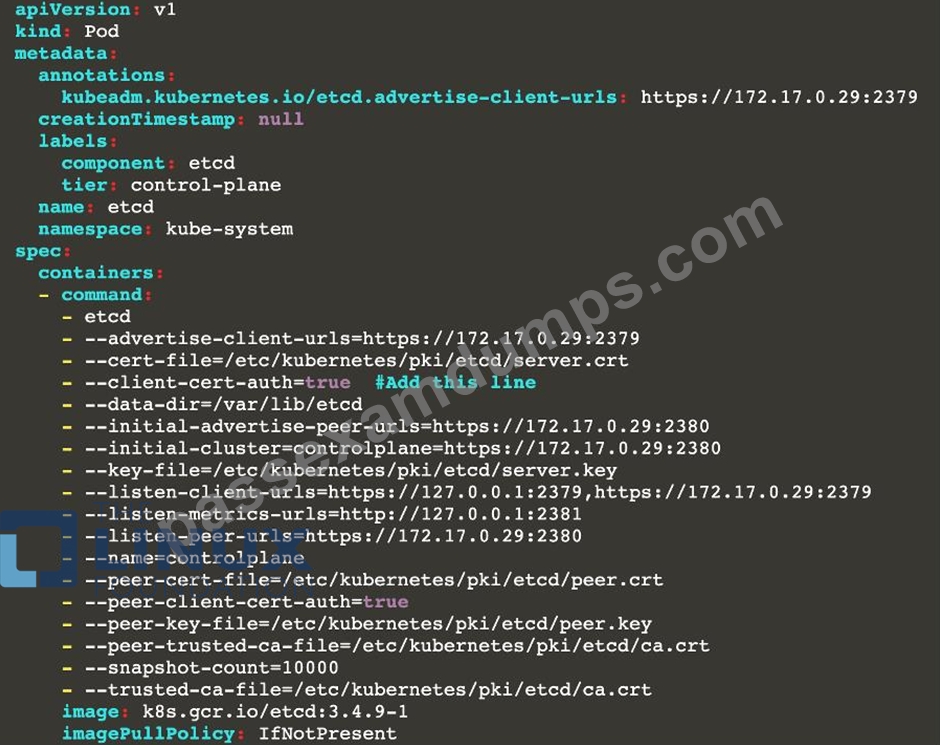
NEW QUESTION # 44
You can switch the cluster/configuration context using the following command: [desk@cli] $ kubectl config use-context stage Context: A PodSecurityPolicy shall prevent the creation of privileged Pods in a specific namespace. Task: 1. Create a new PodSecurityPolcy named deny-policy, which prevents the creation of privileged Pods. 2. Create a new ClusterRole name deny-access-role, which uses the newly created PodSecurityPolicy deny-policy. 3. Create a new ServiceAccount named psd-denial-sa in the existing namespace development. Finally, create a new ClusterRoleBindind named restrict-access-bind, which binds the newly created ClusterRole deny-access-role to the newly created ServiceAccount psp-denial-sa
Answer:
Explanation:
Create psp to disallow privileged container
apiVersion: rbac.authorization.k8s.io/v1
kind: ClusterRole
metadata:
name: deny-access-role
rules:
- apiGroups: ['policy']
resources: ['podsecuritypolicies']
verbs: ['use']
resourceNames:
- "deny-policy"
k create sa psp-denial-sa -n development
apiVersion: rbac.authorization.k8s.io/v1
kind: ClusterRoleBinding
metadata:
name: restrict-access-bing
roleRef:
kind: ClusterRole
name: deny-access-role
apiGroup: rbac.authorization.k8s.io
subjects:
- kind: ServiceAccount
name: psp-denial-sa
namespace: development
Explanation
master1 $ vim psp.yaml
apiVersion: policy/v1beta1
kind: PodSecurityPolicy
metadata:
name: deny-policy
spec:
privileged: false # Don't allow privileged pods!
seLinux:
rule: RunAsAny
supplementalGroups:
rule: RunAsAny
runAsUser:
rule: RunAsAny
fsGroup:
rule: RunAsAny
volumes:
- '*'
master1 $ vim cr1.yaml
apiVersion: rbac.authorization.k8s.io/v1
kind: ClusterRole
metadata:
name: deny-access-role
rules:
- apiGroups: ['policy']
resources: ['podsecuritypolicies']
verbs: ['use']
resourceNames:
- "deny-policy"
master1 $ k create sa psp-denial-sa -n development master1 $ vim cb1.yaml apiVersion: rbac.authorization.k8s.io/v1 kind: ClusterRoleBinding metadata:
name: restrict-access-bing
roleRef:
kind: ClusterRole
name: deny-access-role
apiGroup: rbac.authorization.k8s.io
subjects:
# Authorize specific service accounts:
- kind: ServiceAccount
name: psp-denial-sa
namespace: development
master1 $ k apply -f psp.yaml master1 $ k apply -f cr1.yaml master1 $ k apply -f cb1.yaml Reference: https://kubernetes.io/docs/concepts/policy/pod-security-policy/
NEW QUESTION # 45
Your organization has adopted a microservices architecture. Each microservice is deployed as a Kubernetes pod, and the communication between them relies neavily on service discovery and network policies. You need to implement a security measure to prevent unauthorized pods from accessing sensitive data stored within other pods. What techniques would you use and how would you apply them in a Kubernetes environment?
Answer:
Explanation:
Solution (Step by Step) :
1. Network Policy:
- Define network policies to restrict communication between pods based on specific criteria like namespaces, labels, and pod selectors.
- Create network policies that only allow authorized pods to access sensitive data.
- For example
- Allow pods in the 'production' namespace to only communicate with pods in the same namespace and pods in the 'database' namespace.
- Deny all other tramc from pods in the 'production- namespace.
2. Service Mesh:
- Utilize a service mesh like Istio or Linkerd to provide fine-grained control over service-to-service communication.
- Define policies within the service mesh to enforce authorization rules and restrict access to sensitive data.
- Service mesh implementations offer features like:
- Mutual TLS (mTLS): Encrypt all communications between pods with certificates tor mutual authentication and authorization.
- Traffic Management: Control the flow of traffic between services based on rules, rate limits, and circuit breakers.
- Access Control: Enforce access control policies for specific services or endpoints.
3. Pod security Policies (PSP):
- Implement pod security policies (PSP) to restrict the capabilities and resources available to pods.
- Define PSP rules that prevent pods from accessing sensitive volumes or having privileged permissions.
- Use PSPs to restrict pod resource usage and limit the potential impact of security breaches.
4. Secret Management:
- Store sensitive data, such as API keys, database credentials, and certificates, in Kubernetes secrets.
- Use strong encryption and access control to restrict access to secrets.
- Utilize Kubernetes's built-in secret management tools or third-party solutions to manage and rotate secrets securely.
5. Role-Based Access Control (RBAC)I
- Implement R8AC within Kubernetes to control access to resources.
- Assign roles and permissions to users and service accounts based on their responsibilities.
- Grant minimum privileges to users and service accounts, limiting their access to only what is necessary.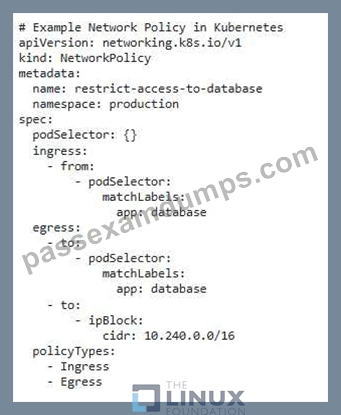
NEW QUESTION # 46
You have a Kubernetes cluster With multiple nodes. You want to configure a Network Policy to allow communication between pods in the "appl" namespace and pods in the "app2" namespace, but only allow access to the port 80 on the pods in the "app2" namespace. Describe the steps you would take to implement this network policy.
Answer:
Explanation:
Solution (Step by Step) :
1. Create a Network Policy YAML file:
- Create a YAML file that defines the Network Policy rules: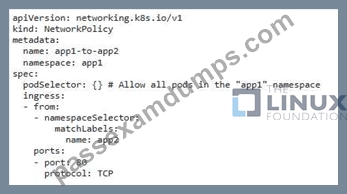
2. Apply the Network Policy: - Apply the YAML file using 'kubectl apply -f app1 -to-app2-yaml' 3. Verify the Network Policy: - After applying the policy, check the status of the network policy using 'kubectl get networkpolicies appl-to-app2 -n app1 4. Test the Policy: - Start a pod in the "app1" namespace and a pod in the "app2" namespace. - Test the communication using tools like 'curl' or 'telnet' to ensure that the policy restricts access to only pod 80 on pods in "app2". 5. Add More Restrictions (Optional): - You can further refine the Network Policy by specifying more restrictive rules, such as allowing access only from specific pods in "app1" or restricting access to specific IP addresses in "app2".
NEW QUESTION # 47
You are deploying a Kubernetes cluster on AWS using EKS. verify the authenticity and integrity of the AWS CLI and EKS platform binaries before interacting with your cluster:
Answer:
Explanation:
Solution (Step by Step):
I). Install the AWS CLI: Download and install the AWS CLI from the official website ([https://aws.amazon.com/clif](https://www.google.com/url?
sa=E&source=gmail&q=https://aws.amazon.com/cli/)).
2. Verify the AWS CLI installation: Use the aws -version' command to check the version and ensure it is installed correctly.
3. Configure AWS credentials: Configure your AWS credentials using the saws configure' command.
4. Verify the EKS API server endpoint: Use the 'aws eks describe-cluster command to retrieve the API server endpoint for your EKS cluster_ Verity
that the endpoint matches the expected format and domain name for your region.
bash
aws ekS describe-cluster -name my-cluster -query "cluster. endpoint" -output text
5. Verify the authenticity of the EKS API server certificate: Retrieve the EKS API server certificate using the 'openssl s_client command and verity the certificate chain and issuer.
bash
openssl s_client -connect :443 /dev/null | openssl x509 -in - -text -noout
6. (Optional) Use the AWS CLI to further validate EKS components: You can use the AWS CLI to check the status and configuration of other EKS components, such as the control plane, worker nodes, and networking.
NEW QUESTION # 48
You are using a managed Kubernetes offering like Google Kubernetes Engine (GKE)- Implement a process to verify the integrity of the GKE platform binaries and components.
Answer:
Explanation:
Solution (Step by Step):
1. Enable node auto-upgrade: Configure your GKE cluster to automatically upgrade nodes to the latest stable version. This ensures that security updates and bug fixes are applied promptly.
bash
gcloud container clusters update my-cluster -release-channel regular
2. Use the gcloud CLI to inspect cluster components: Use the 'gcloud container clusters describe' command to retrieve information about your GKE cluster, including the Kubernetes version, node image, and control plane version. Verify that these versions are up-to-date and consistent with your expectations.
bash
gcloud container clusters describe my-cluster
3. Review GKE release notes: Regularly review the GKE release notes ([https://cloud.google.com/kubernetes-engine/docs/release-notes]
(https://www.google.com/url?sa=E&source=gmail&q=https://cloud.google.com/kubernetes.engine/docs/release-notes)) to stay informed about security updates, bug fixes, and new features.
4. Enable GKE security features: Utilize GKE security features like Shielded GKE Nodes, Container-optimized OS security hardening, and Binary Authorization to enhance the security of your cluster.
5. Monitor GKE security advisories: Subscribe to Google Cloud security advisories and bulletins to stay informed about any potential vulnerabilities or security issues affecting GKE.
NEW QUESTION # 49
You are setting up a Kubernetes cluster that requires strong security measures. You need to implement several security best practices, including.
- Pod Security Policy: Implement a default Pod Security Policy that restricts resource requests, limits privilege escalation, and disables container root access.
- Network Policy: Configure network policies to restrict communication between pods within the cluster, enforcing a principle of least privilege.
- Admission Controller: Use the 'PodSecurityPolicys admission controller to enforce the defined Pod Security Policy rules.
How would you set up a secure Kubernetes cluster, including the configuration of a default Pod Security Policy, network policies, and the 'PodSecuntyP01icy' admission controller, to enforce these security best practices?
Answer:
Explanation:
Solution (Step by Step) :
1. Create a Default Pod Security Policy:
- Create a YAML file named 'psp.yaml' with the following content: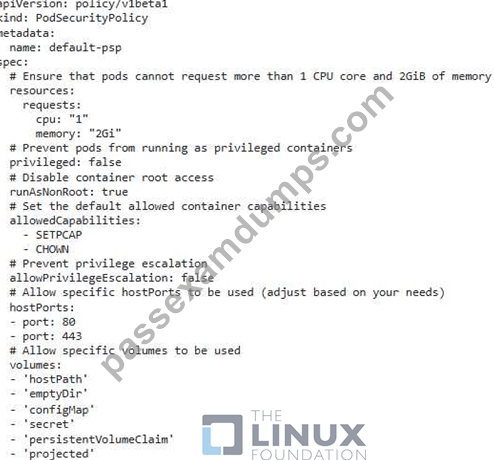
2. Create Network Policies: - Create separate YAML files for each network policy you need. - For example, a policy to restrict communication between pods in the 'frontend' and 'backend' namespaces could be defined as: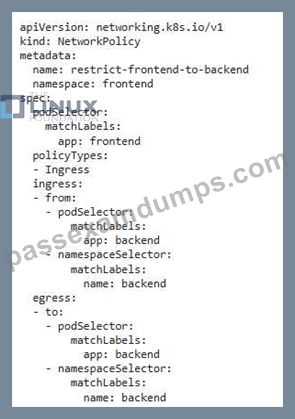
3. Enable the 'PodSecurityPolicy' Admission Controller: - Modify the Kubernetes API server configuration (e.g., vetc'kubernetes/manifests/kube-apiserver.yaml') to enable the 'PodSecurityPolicy' admission controller: - Add the following line: '--admission-control=NamespaceLifecycle,LimitRanger,ServiceAccount,PodSecurityPolicy' 4. Apply the Configuration: - Apply the 'psp.yaml' and network policy files to the cluster using 'kubectl apply -f -yamr - Restart the Kubernetes API server for the changes to take effect. 5. Test the Configuration: - Try to create a pod that violates the Pod Security Policy rules. - You should see an error message indicating that the PodSecurityPolicy is preventing the pod creatiom - Test the network policies by attempting to communicate between pods and verifying that traffic is restricted according to the defined rules. 6. Monitor and Adjust - Monitor the cluster for any potential issues caused by the security policies. - Adjust the policies as needed based on evolving security requirements and application needs. Note: It's recommended to use a tool like 'kubectl apply -f -s to pipe the content of the YAML files to the command for applying the resources.
NEW QUESTION # 50
You have a container named 'my-container that runs a process with elevated privileges. The container image is based on a custom base image that includes a vulnerable library. You need to implement a security policy to restrict the container from accessing the vulnerable library and to prevent it from running with elevated privileges.
Answer:
Explanation:
Solution (Step by Step) :
1. Create a SecurityContext for the container: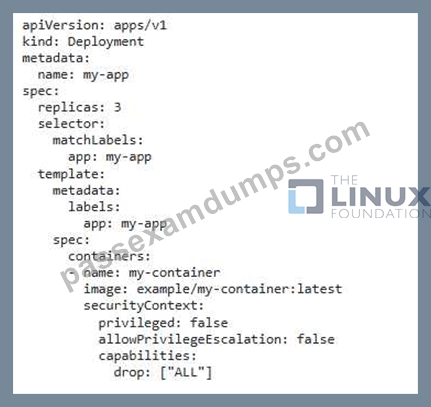
2. Modify the Dockerfile to remove the vulnerable library: - Update your Dockerfile to remove the vulnerable library from the image. 3. Rebuild the image and push it to a registry: - Rebuild the image using the updated Dockerflle. - Push the updated image to your registry. 4. Apply the updated Deployment bash kubectl apply -f my-app-deployment.yaml - 'privileged: false': Prevents the container from running with root privileges. - 'allowPrivilegeEscalation: false: Disables the container's ability to escalate its privileges. - 'capabilities: drop: ["ALL"]': Removes all capabilities from the container. - Removing the vulnerable library from the Dockerfile: Prevents the container from accessing the vulnerable library during runtime. Important Notes: - These measures aim to restrict the containers access to vulnerable libraries and prevent it from running with elevated privileges. - It's crucial to update your base image and dependencies regularly to mitigate vulnerabilities. - You might need to adjust the 'capabilities' list based on the specific requirements of the container. - Always test your security policies thoroughly to ensure they are effective and do not break your application functionality.
NEW QUESTION # 51
......
Fully Updated Free Actual Linux Foundation CKS Exam Questions: https://www.passexamdumps.com/CKS-valid-exam-dumps.html
Free CKS Questions for Linux Foundation CKS Exam [May-2026]: https://drive.google.com/open?id=1RQ7BR9EtXD_cuZPKA9MYwkET4PJbKiCY
